WP Manifestindependent plugin directory
manifest / analytics / servertrack

Ratul Ads Conversion Tracker WP Registry grade D+. High-severity findings · 4 findingsWP RegistryHigh-severity findings · 4 findingsOpen the reportD+

lets not waste money on server side tracking and data de duplication. I , Yaser Ahmmed Ratul Invented this plugin in order to replace a 20$ monthly shit for free of cost for the digital marketers. enjoy !

★ 4stars
8release downloads
6.0.4latest · 3mo ago

Install

Download ServerTrack-6Typhon.zip From the 6.0.4 release on GitHub, Jul 15, 2026

Upload it under Plugins → Add New Plugin → Upload Plugin, then activate.

Install straight from GitHub with WP-CLI:

wp plugin install https://github.com/yaratul2005/servertrack/releases/download/6.0.4/ServerTrack-6Typhon.zip
No built-in updater. New versions won't appear under Dashboard → Updates. Install new releases yourself, or let Git Updater track the repository.

Ratul Ads Conversion Tracker (Ratul-ACT)
WordPress Compatibility PHP Compatibility WooCommerce Compatibility Ad-Blocker Resiliency

Meta Conversions API TikTok Events API Google Ads Enhanced Conversions


🌟 Executive Summary

Ratul Ads Conversion Tracker (Ratul-ACT) is a self-hosted, enterprise-grade first-party Conversion API (CAPI) and browser tracking gateway for WordPress and WooCommerce.
Designed to bypass ad-blockers and privacy regulations (iOS 14+, Safari ITP), Ratul-ACT routes tracking events directly through your own domain. It synchronizes browser event ids and server dispatches to provide Meta, Google, and TikTok with perfect deduplication data. By eliminating dependency on expensive external tag containers like Stape.io or Google Cloud GTM, it acts as a direct, self-hosted CAPI engine on your WordPress server.


🚀 Key Features & Capabilities

Feature Description Business Benefit
First-Party Cookie Engine Issues first-party Set-Cookie headers directly via PHP, protecting tracking identifiers (fbclid, gclid) from Safari's 7-day script caps. Extends attribution lifespans to 2 years
Ad-Blocker Resilience Proxies client-side events through a local WordPress REST endpoint. Recovers up to 20–30% of lost checkout signals
Signal Enrichment Extracts IP, City, State, ZIP, and User-Agent parameters dynamically on the client, with fallbacks for Cloudflare and Nginx. Maximizes Meta Event Match Quality (EMQ)
Anti-Fraud Approval Prevents automatic purchase tracking, allowing manual confirmation and fraud checks from the admin order screen. Prevents fake/refunded orders from polluting ad algorithms
Fail-Safe Retry Queue Exponential back-off retry loop that automatically resends failed platform payloads. Guarantees delivery of server-side conversions

📊 Live Verification & Deduplication

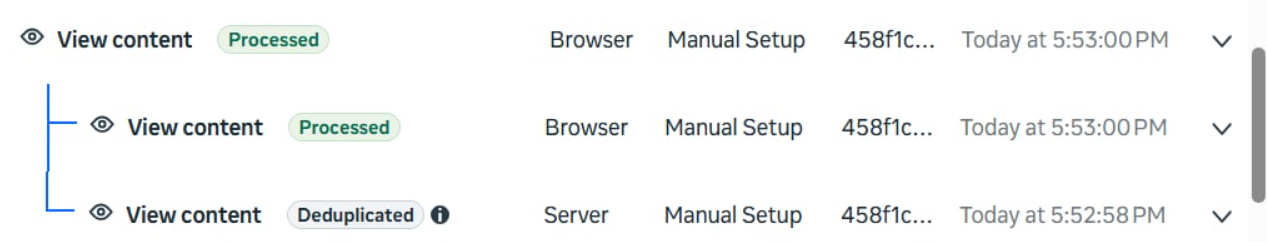
1. Meta Event Manager Deduplication

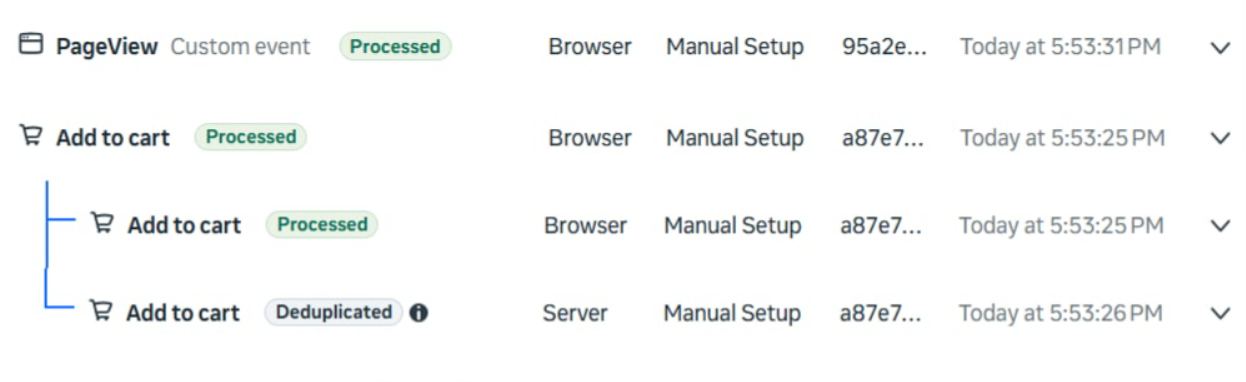
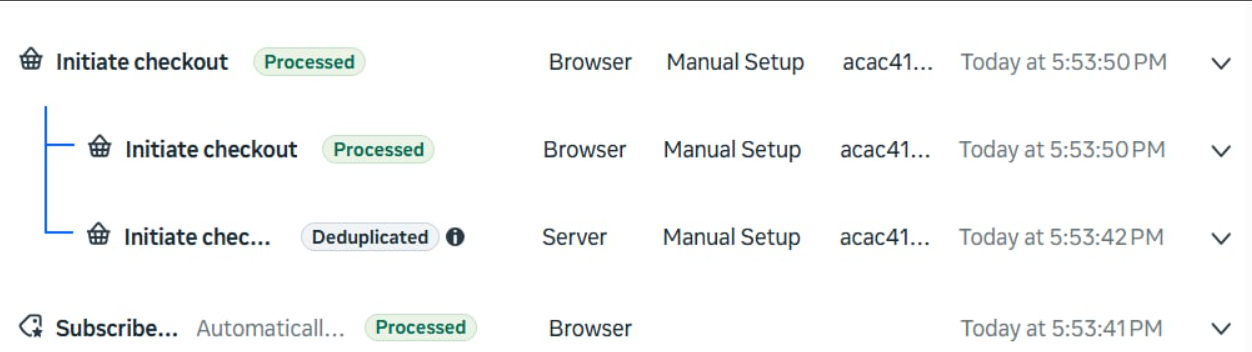
Both client-side browser triggers and server-side CAPI webhooks report matching Event IDs, allowing Meta to successfully deduplicate actions:

  • View Content: ViewContent Deduplication
  • Add to Cart: AddToCart Deduplication
  • Initiate Checkout: InitiateCheckout Deduplication

🖥️ UI Dashboard & Configuration

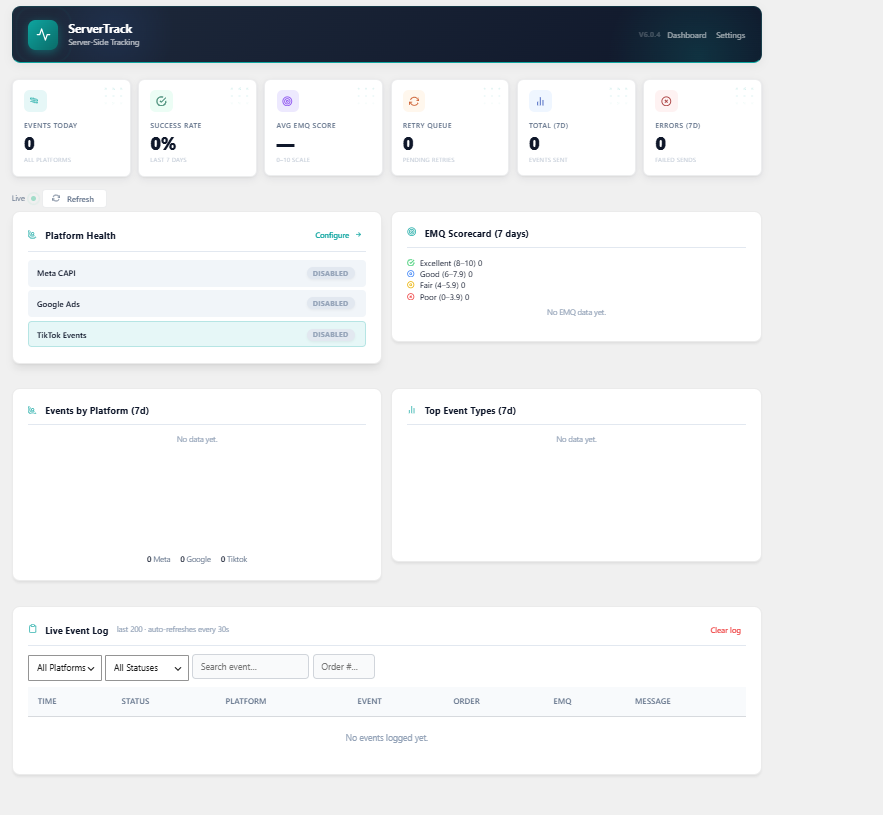
Real-Time Performance Analytics

Inspect event metrics, health stats, API response logs, and queue retries in real-time. Real-Time Dashboard
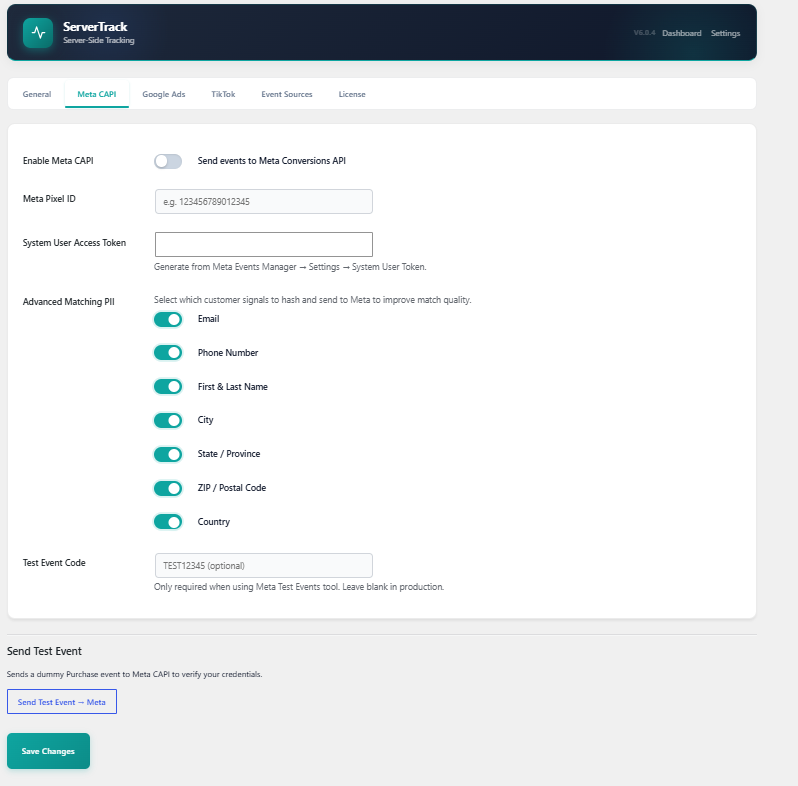
Multi-Pixel Meta CAPI Setup

Loop dispatches to multiple Meta Pixels with toggle controls for PII parameter hashing. Meta Settings
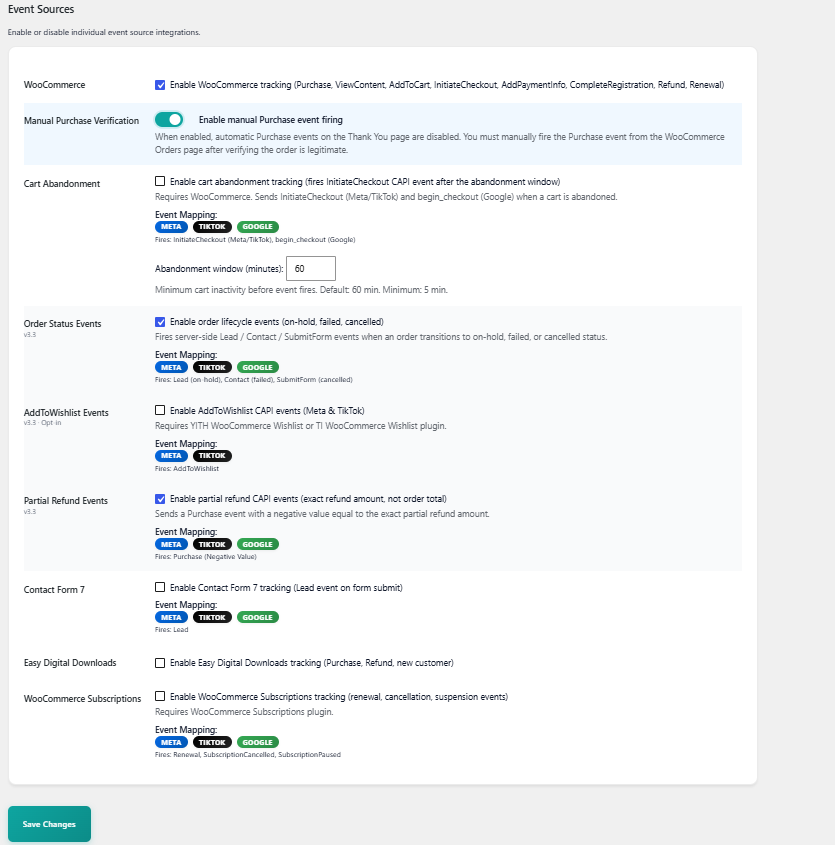
WooCommerce Advanced Sources

Configure extended WooCommerce triggers (order lifecycle status, wishlist opt-ins) and toggle Manual Purchase Verification. WooCommerce Event Sources Settings

🛠️ Installation & Activation

  1. Upload the ratul-ads-conversion-tracker directory to /wp-content/plugins/.
  2. Activate the plugin via Plugins → Installed Plugins.
  3. Go to Ratuls-ACT → Settings to set up your ad platform access tokens.
  4. Monitor active events and match metrics in Ratuls-ACT → Dashboard.

📚 Technical Documentation

To explore the deeper mechanics of the plugin, refer to the accompanying documentation files:

  • 🛠️ ARCHITECTURE.md: Details the codebase design, data flows, database deduplication engine, and ITP cookie bypass logic.
  • 🛡️ COMPLIANCE.md: Explains GDPR/CCPA cookie consent manager integrations (CookieYes, Complianz) and the data security PII blocklist.

📄 License & Credits

Licensed under GPL-2.0-or-later. Created and maintained by MD. Yaser Ahmmed Ratul.

Releases

2 releases. Each count is every asset in that release; expand a row for the breakdown.

Tag
Published
Assets
Downloads
6.0.4 latest
Jul 15, 2026 3mo ago
ServerTrack-6Typhon.zip
4
May 9, 2026 5mo ago
ServerTrack-main.1.zip
4
D+ grade

Security

Ratul Ads Conversion Tracker 6.0.4 · audited by WP Registry

High-severity findings.

2 high 2 medium
Audited release
6.0.4
Findings
4
Worst severity
high
Content hash
1d410c5d18c6b1a96ac01cc7…

Findings

  • high Unauthenticated CAPI conversion injection via public /custom-event REST route

    missing_permission_callback

    POST /wp-json/ratul-ads-conversion-tracker/v1/custom-event is registered with permission_callback __return_true. The handler accepts allowlisted event names that include Purchase, InitiateCheckout, Lead, Donate, and StartTrial, merges attacker-controlled params (including value/currency) into custom_data, and immediately calls Ratul_ACT_Meta::send / Ratul_ACT_TikTok::send when those platforms are enabled. Default consent_mode is 'none', so Ratul_ACT_Consent::is_granted() returns true even on REST requests. The only control is a 10-token rate limiter keyed on md5(client_ip + hashed User-Agent). get_request_ip() prefers HTTP_CF_CONNECTING_IP then HTTP_X_REAL_IP then the last X-Forwarded-For token — all client-controlled on a default WordPress host that is not behind Cloudflare/nginx stripping those headers. Independently, rotating User-Agent mints a new bucket, so the limiter does not bound an attacker. Observable consequence: fake Purchase events with arbitrary value appear in the merchant's Meta/TikTok Events Manager and in option ratul_act_debug_log, using the stored ratul_act_meta_access_token / ratul_act_tiktok_access_token, which can poison attribution and cause conversion-optimized campaigns to spend against fraudulent conversions. Sibling public route POST /pixel/{platform} is the same class of CAPI proxy (no event-name allowlist) but currently fatals because it calls private Ratul_ACT_Frontend::get_request_ip().

    frontend/class-ratul-act-frontend.php:150-254

    Recommendation

    Do not accept Purchase/Lead/Donate (or any value-bearing conversion) from an unauthenticated browser bridge. Require a real WooCommerce/EDD session proof or a per-event server-issued nonce bound to cart/order state. Rate-limit exclusively on the TCP peer (REMOTE_ADDR) unless the site operator has explicitly configured a trusted proxy, and do not include User-Agent in the bucket key. Keep platform send() behind that gate so stored CAPI tokens cannot be used as an open conversion API.

  • high Unauthenticated WooCommerce order data disclosure on order-received page

    information_disclosure

    enqueue_pixel_script() runs on every frontend request. When is_order_received_page() is true it reads get_query_var('order-received') as an order ID, loads the order with wc_get_order(), and localizes value, currency, order_id, contents (SKU, quantity, item_price), content_ids, event_id, and gclid into the public ratul_act_config JavaScript object. WooCommerce's is_order_received_page() is true whenever the checkout order-received endpoint is in the query vars; it does not verify $_GET['key'] against the order key (that check happens later in the thankyou template, after scripts are enqueued). Sequential order IDs can therefore be enumerated at /checkout/order-received/{id}/ without the wc_order key. Observable consequence: any visitor can read another customer's purchase total, line items, and stored Google click ID from page source / ratul_act_config, even when WooCommerce itself renders the invalid-order screen. This path does not require advertising platforms to be enabled (ratul_act_enabled defaults to 1).

    frontend/class-ratul-act-frontend.php:449-492

    Recommendation

    Before localizing any order fields, require a matching order key (hash_equals($order->get_order_key(), wc_clean(wp_unslash($_GET['key'] ?? '')))) and the same visibility rules WooCommerce uses for the thank-you page (logged-in owner or valid guest key). Do not enqueue purchase payloads for invalid or other users' orders.

  • medium Hardcoded CRXSM license-server client credentials

    hardcoded_credentials

    Ratul_ACT_License::get_client() embeds a client_id, HMAC client_secret, and Ed25519 public_key used to sign activate/deactivate/heartbeat requests to https://great10.xyz/Tunnel/index.php. Anyone with the plugin package can impersonate this software to the license tunnel (forge signed API calls for arbitrary domains). These secrets do not grant WordPress admin on customer sites, and is_active() only drives the License settings UI rather than gating CAPI sends. They are still long-lived credentials shipped in every install.

    includes/class-ratul-act-license.php:23-29

    Recommendation

    Treat the license HMAC secret as a server-side credential that must not ship in publicly distributed plugin copies, or accept that the tunnel cannot authenticate the client at all and rely only on the offline Ed25519 license signature. Rotate the exposed client_secret on the license server.

  • medium Unauthenticated REST endpoints set first-party attribution cookies

    cookie_injection

    POST /wp-json/ratul-ads-conversion-tracker/v1/capture-clickids (permission_callback __return_true, no nonce) reads JSON ids.fbclid/ttclid/gclid/msclkid/ScCid and calls setcookie() for _fbc, _ttclid, _gcl_aw, msclkid, and _sccid (90-day, path=/, httponly=false). WordPress REST reflects arbitrary Origin with Access-Control-Allow-Credentials: true, so a third-party page can credentialed-POST and toss those cookies onto a shop visitor. That lets an attacker bind the victim's subsequent Purchase CAPI events to the attacker's click IDs (attribution theft). Related public POST /capture writes the same identifiers into user meta for logged-in users and into a transient keyed by attacker-supplied session_id, and /capture-pii writes a hashed email into the WooCommerce session.

    frontend/class-ratul-act-frontend.php:102-130

    Recommendation

    Do not set first-party cookies from a CORS-open REST body. Capture click IDs only from same-request URL parameters in PHP (CookieHelper already does this) or require a same-origin nonce that is not sent to other origins. Reject cross-origin credentialed calls (do not rely on core REST CORS).

WP Registry hashes the installable build and reports on that exact bytes-for-bytes copy. Embargoed findings are withheld until they are disclosed, so a clean verdict means nothing public is outstanding. WP Manifest does not audit code itself.