WP Manifestindependent plugin directory
manifest / media / wp-parsaspace

ParsaSpace CDN Host WP Registry grade D+. High-severity findings · 3 findingsWP RegistryHigh-severity findings · 3 findingsOpen the reportD+

اتصال کتابخانه رسانه های وردپرس به هاست دانلود پارسااسپیس

★ 11stars
1.7krelease downloads
≈220active sites
v2.3.0latest · 6 years ago

Install

Download wp-parsaspace-v2.3.0.zip From the v2.3.0 release on GitHub, Jul 23, 2020

Upload it under Plugins → Add New Plugin → Upload Plugin, then activate.

Install straight from GitHub with WP-CLI:

wp plugin install https://github.com/mehrshaddarzi/wp-parsaspace/releases/download/v2.3.0/wp-parsaspace-v2.3.0.zip
Updates itself. It ships its own updater, so new versions appear under Dashboard → Updates.

افزونه پارسااسپیس کتابخانه های رسانه های وردپرس را به هاست دانلود متصل می کند و فایل های رسانه های وردپرس بطور کاملا هماهنگ در سرور های پارسااسپیس مدیریت می شود.اگر یک وب سایت دانلود محتوا دارید و یا بازدید و پهنای باند زیادی در وب سایت وردپرس خود مصرف می کنید نصب این افزونه می تواند سرعت وب سایت وردپرس شما را بسیار بهبود ببخشد.
امکانات افزونه پارسااسپیس :
  • 1. قابلیت آپلود بهنگام رسانه های وردپرس در هاست دانلود
  • 2. هماهنگی کامل با افزونه های فشرده ساز تصاویر وردپرس
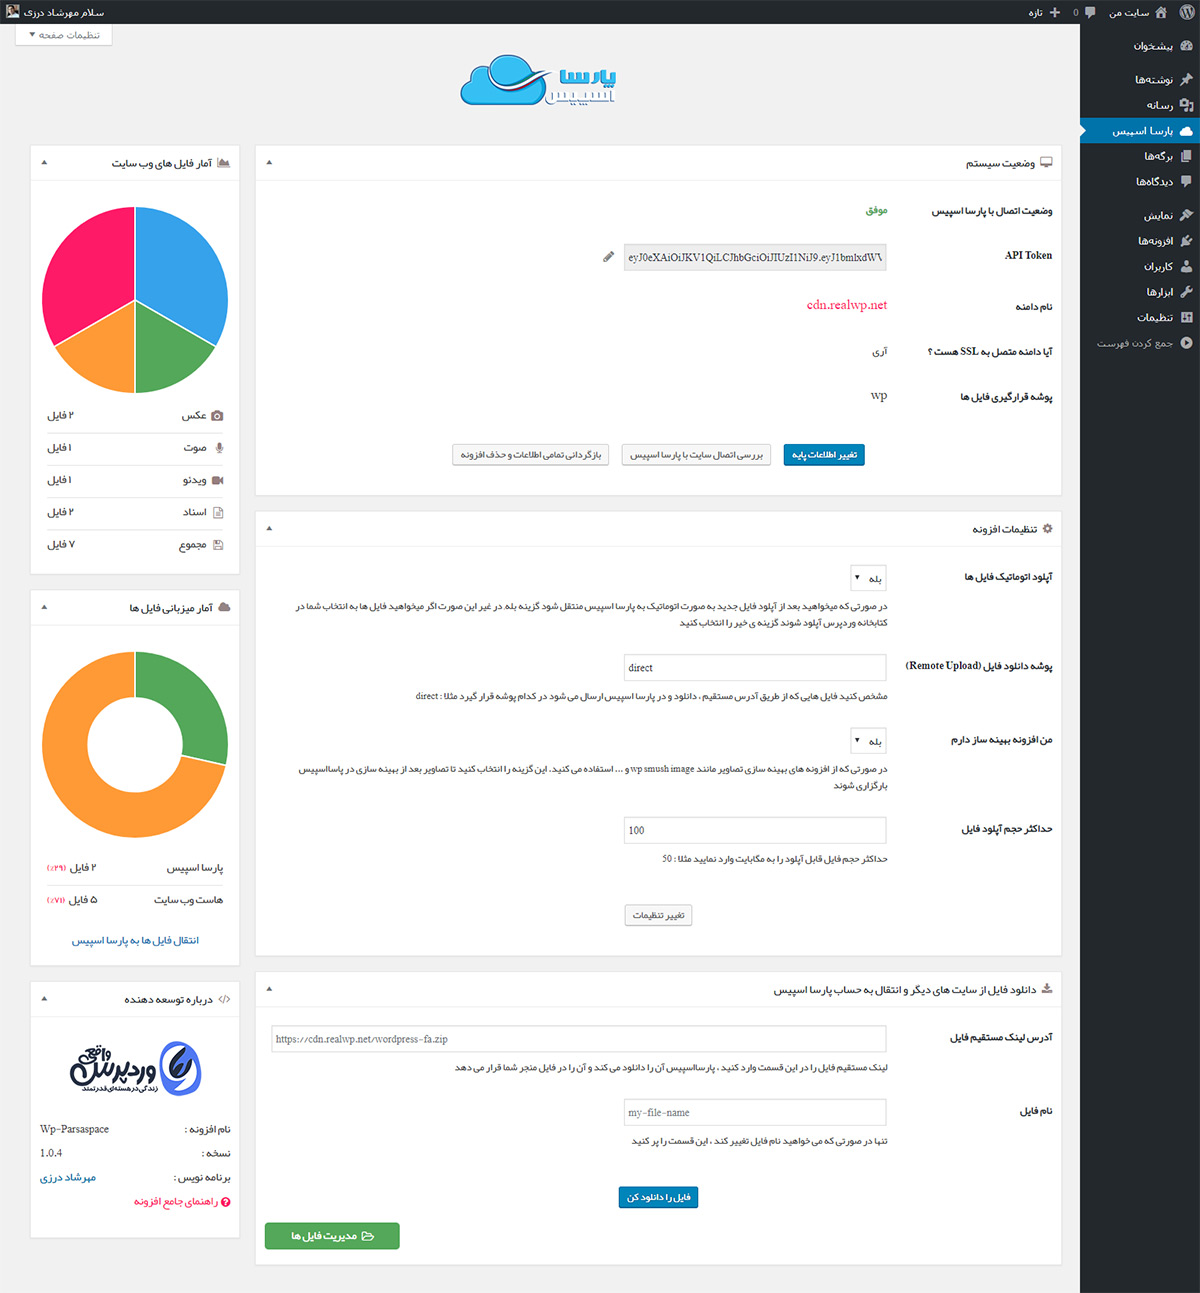
  • 3. گزارش کامل از وضعیت فایل های رسانه های شما به صورت گرافیکی
  • 4. قابلیت انتقال فایل های وردپرس به انتخاب کاربر
  • 5. امکان دانلود فایل از وب سایت های دیکر یا ریموت دانلود
  • 6. هماهنگی کامل با لینک های موجود در پایگاه داده وردپرس و عدم شکسته شدن لینک فایل ها بعد از جابه جایی

راهنمای کار با افزونه :
راهنمای جامع کار و نصب افزونه پارسا اسپیس را از اینجا مطالعه کنید

پیش نیاز نصب افزونه پارسا اسپیس :
  • 1. نصب PHP نسخه ی 5.4 بالاتر
  • 2. فعال بودن تابع Curl در php
  • 3. یک اکانت در سایت پارسااسپیس ایجاد کنید تا یک کد API دریافت کنید
  • 4. این افزونه در Localhost کامپیوتر قابلیت فعال سازی ندارد

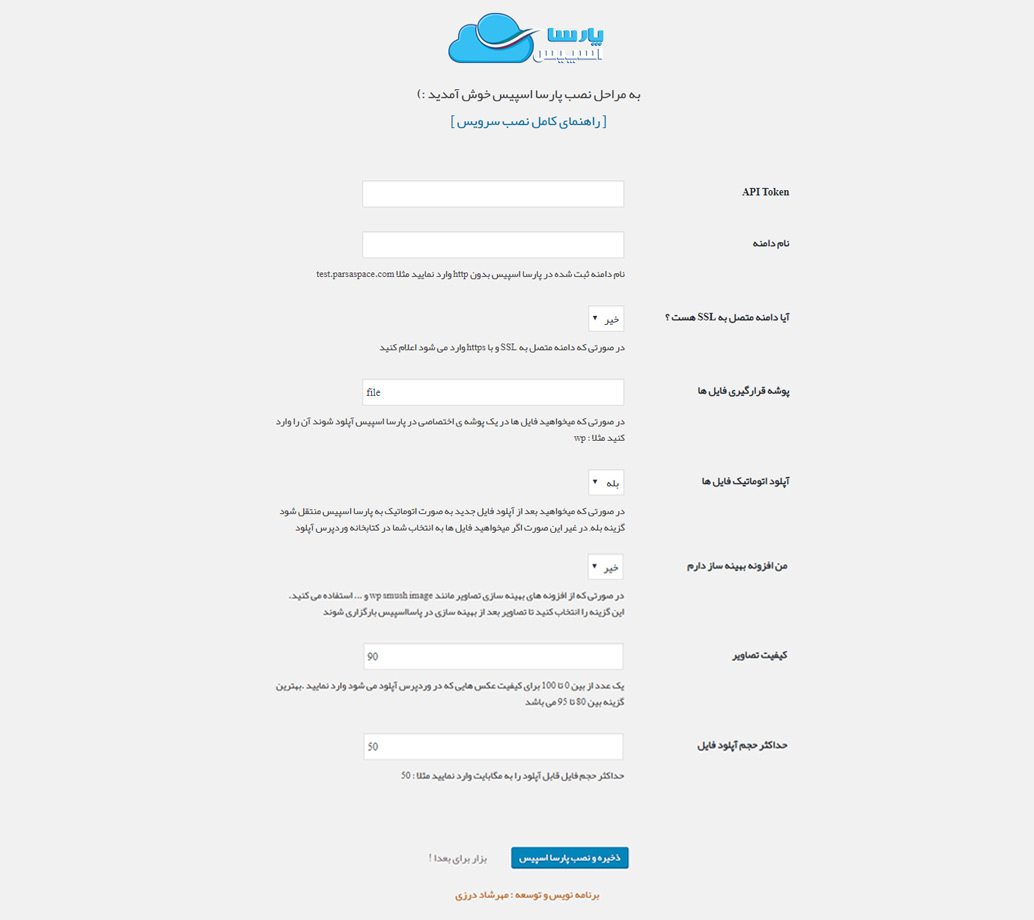
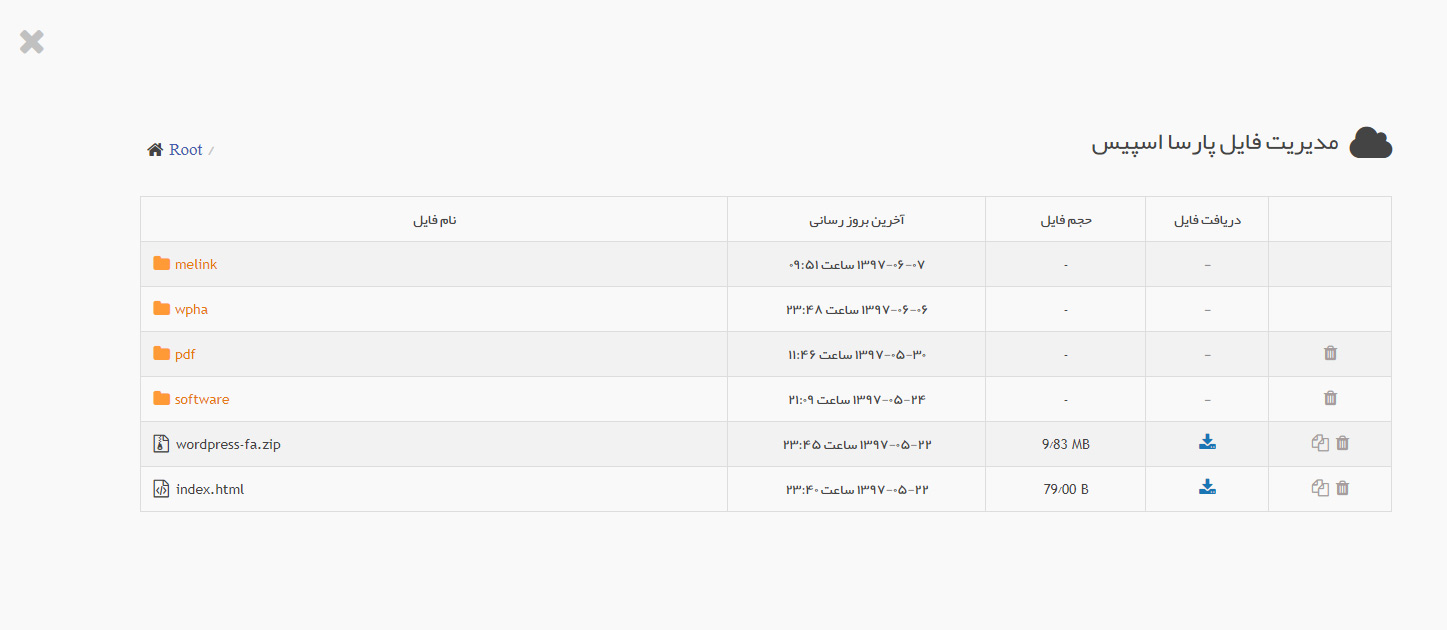
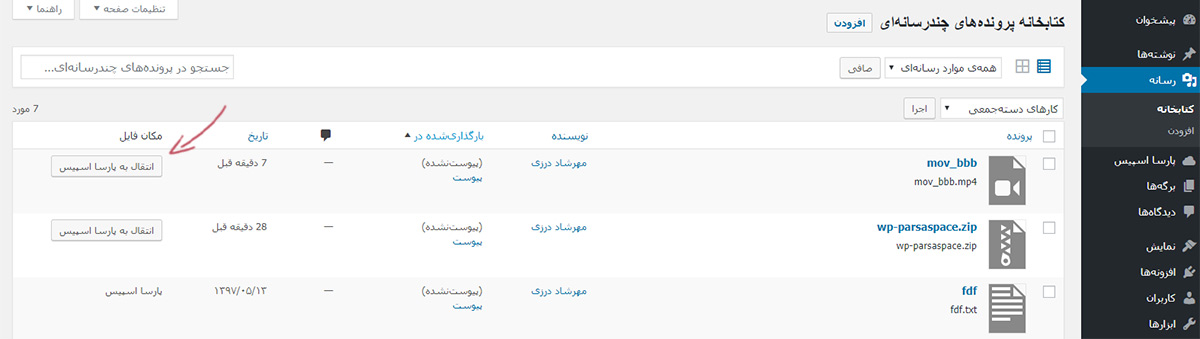
تصاویر محیط افزونه
Releases

5 releases. Each count is every asset in that release; expand a row for the breakdown.

Tag
Published
Assets
Downloads
v2.3.0 latest
Jul 23, 2020 6 years ago
wp-parsaspace-v2.3.0.zip
773
May 5, 2020 6 years ago
wp-parsaspace-v2.2.1.zip
90
Aug 24, 2019 7 years ago
wp-parsaspace-v2.2.0.zip
381
2.0
Feb 27, 2019 7 years ago
wp-parsaspace-v2.0.zip
288
Nov 22, 2018 7 years ago
wp-parsaspace-v1.0.6.zip
154

Active-site estimate ≈220 comes from the median of recent superseded releases. Method.

D+ grade

Security

ParsaSpace CDN Host 2.3.0 · audited by WP Registry

High-severity findings.

3 high
Audited release
2.3.0
Findings
3
Worst severity
high
Content hash
f1c53f5e01e0e44a99c4cd7c…

Findings

  • high Subscriber+ can run all ParsaSpace AJAX actions: CDN settings, sitewide URL replace, and remote file delete

    missing_capability

    Wp_Parsaspace_Admin_Ajax registers ten wp_ajax_* actions from a method whitelist. Every handler's only gate is check_ajax_referer('wp_parsaspace_token','security'); none call current_user_can. The matching nonce is localized as wp_parsaspace_ajax.security inside enqueue_scripts on every wp-admin page (chart.js is limited to toplevel_page_parsaspace_setting; the nonce is not). A Subscriber visiting /wp-admin/profile.php therefore receives a usable nonce and can GET admin-ajax.php as themselves. Observable without a ParsaSpace account: change_parsaspace_setting_form writes is_optimize/quality_jpg/max_size_upload/remote_dir into autoloaded wp_parsaspace_opt (upload_size_limit then does remove_all_filters('upload_size_limit') and returns 1024*1024*max_size_upload for the whole site); reset_all_url_in_db_parsaspace DELETEs all cdn_parsaspace postmeta and REPLACE()s the current CDN base URL with wp_upload_dir()['baseurl'] across posts.post_content and postmeta.meta_value. If the site is already connected, the same caller uses the stored Bearer token as a confused deputy: change_setting_domain_parsaspace / install_parsaspace overwrite api_token/domain_name/is_ssl/base_folder (front-end get_attachment_url then prefixes every attachment with that host), wp_remove_path_parsaspace deletes an arbitrary CDN path, wp_parsaspace_filemanager_api lists the bucket, and transfer_to_parsaspace rewrites a chosen attachment's URL. The settings UI is manage_options-only; that cap is never checked on the AJAX path.

    includes/class-wp-parsaspace-admin-ajax.php:11-26,36-127,136-210,347-437,446-479,797-835

    Recommendation

    Require current_user_can('manage_options') (or a dedicated cap) in every AJAX handler before any option/DB/API work, in addition to the nonce. Only localize wp_parsaspace_ajax on toplevel_page_parsaspace_setting for users who pass that cap. Do not interpolate URLs into SQL; use $wpdb->prepare or a safe replace helper.

  • high Subscriber+ SSRF: remote-upload AJAX makes the site HEAD any URL, then asks ParsaSpace to fetch it

    ssrf

    request_remote_url_to_parsaspace is one of the nonce-only wp_ajax actions. After empty-checks it assigns $file_url = trim($_GET['file_url']) with no wp_http_validate_url, scheme allowlist, or host blocklist. Helper::curl_get_file_size() curl_init's that URL with CURLOPT_NOBODY and CURLOPT_FOLLOWLOCATION (max 3 redirects) from the WordPress server — so a Subscriber can probe http://127.0.0.1, http://169.254.169.254/, http://[::1]/, and other internal endpoints via status/size. If the HEAD reports a non-zero Content-Length, Api::CreateFolder + Api::RemoteUpload POST the same attacker URL to http://api.parsaspace.com/v1/remote/new using the site's stored Bearer token, causing the CDN to retrieve it. file_name is optional; when omitted the remote basename is kept. Observable as Subscriber with the localized nonce: GET admin-ajax.php?action=request_remote_url_to_parsaspace&security=<nonce>&file_url=http://<internal>&file_name=.

    includes/class-wp-parsaspace-admin-ajax.php:489-583

    Recommendation

    Gate the handler with manage_options. Validate file_url with wp_http_validate_url (HTTPS only) and reject loopback, link-local, private, and non-http(s) schemes. Do not follow redirects to those destinations. Prefer wp_safe_remote_head over raw curl.

  • high Subscriber can store admin XSS in remote_dir; file manager HTML is inserted via jQuery.html

    xss_stored

    change_parsaspace_setting_form (nonce-only, no TestApi) sets wp_parsaspace_opt['remote_dir'] to remove_slash(trim($_GET['remote_dir'])), which strips / and \ but leaves quotes, angle brackets, and event handlers. meta_box_system echoes that value into an unescaped input: value="'.$opt['remote_dir'].'". The settings page is manage_options, so when an administrator opens ParsaSpace → settings the payload runs in the admin session (e.g. " autofocus onfocus="…. request_remote_url_to_parsaspace then CreateFolder('/'+remote_dir), so a folder with the same name appears in the file manager. wp_parsaspace_filemanager_api concatenates unsanitized $_GET['path'] and $l['Name'] into HTML attributes and cell text; admin/js/wp-parsaspace-admin.js assigns the JSON text field with $(".parsaspace_content_file_manager").html(data['text']), which executes inline event handlers (and historically script nodes). That is a reliable admin-session XSS after the Subscriber write, i.e. site takeover once an admin visits the plugin screen or opens the file manager.

    admin/class-wp-parsaspace-admin-ui.php:318-322

    Recommendation

    Sanitize remote_dir to a safe folder slug (alphanumeric/dash) on write. Escape option values with esc_attr/esc_html on output. Escape file-manager names/paths before building HTML, or switch the JS consumer to .text() / DOM APIs. Still require manage_options on the write AJAX.

WP Registry hashes the installable build and reports on that exact bytes-for-bytes copy. Embargoed findings are withheld until they are disclosed, so a clean verdict means nothing public is outstanding. WP Manifest does not audit code itself.