WP Manifestindependent plugin directory
manifest / admin / dt-setup-wizard

Disciple.Tools - Setup Wizard WP Registry grade D+. High-severity findings · 2 findingsWP RegistryHigh-severity findings · 2 findingsOpen the reportD+

Speed up your new site setup process through a multi-step wizard interface.

★ 0stars
138release downloads
≈10active sites
v1.0.2latest · 2 years ago

Install

Download disciple-tools-setup-wizard.zip From the v1.0.2 release on GitHub, Jul 25, 2024

Upload it under Plugins → Add New Plugin → Upload Plugin, then activate.

Install straight from GitHub with WP-CLI:

wp plugin install https://github.com/cairocoder01/dt-setup-wizard/releases/download/v1.0.2/disciple-tools-setup-wizard.zip
Updates itself. It ships its own updater (Plugin Update Checker), so new versions appear under Dashboard → Updates.

Plugin Banner

Disciple.Tools - Setup Wizard

Speed up your new site setup process through a multi-step wizard interface.

Purpose

Streamline the setup of new sites by creating a JSON configuration that will generate a multi-step wizard process. Go through each step and optionally implement all, some, or none of the options in the given step.

Usage

Will Do

  • Generate multi-step wizard interface from JSON configuration
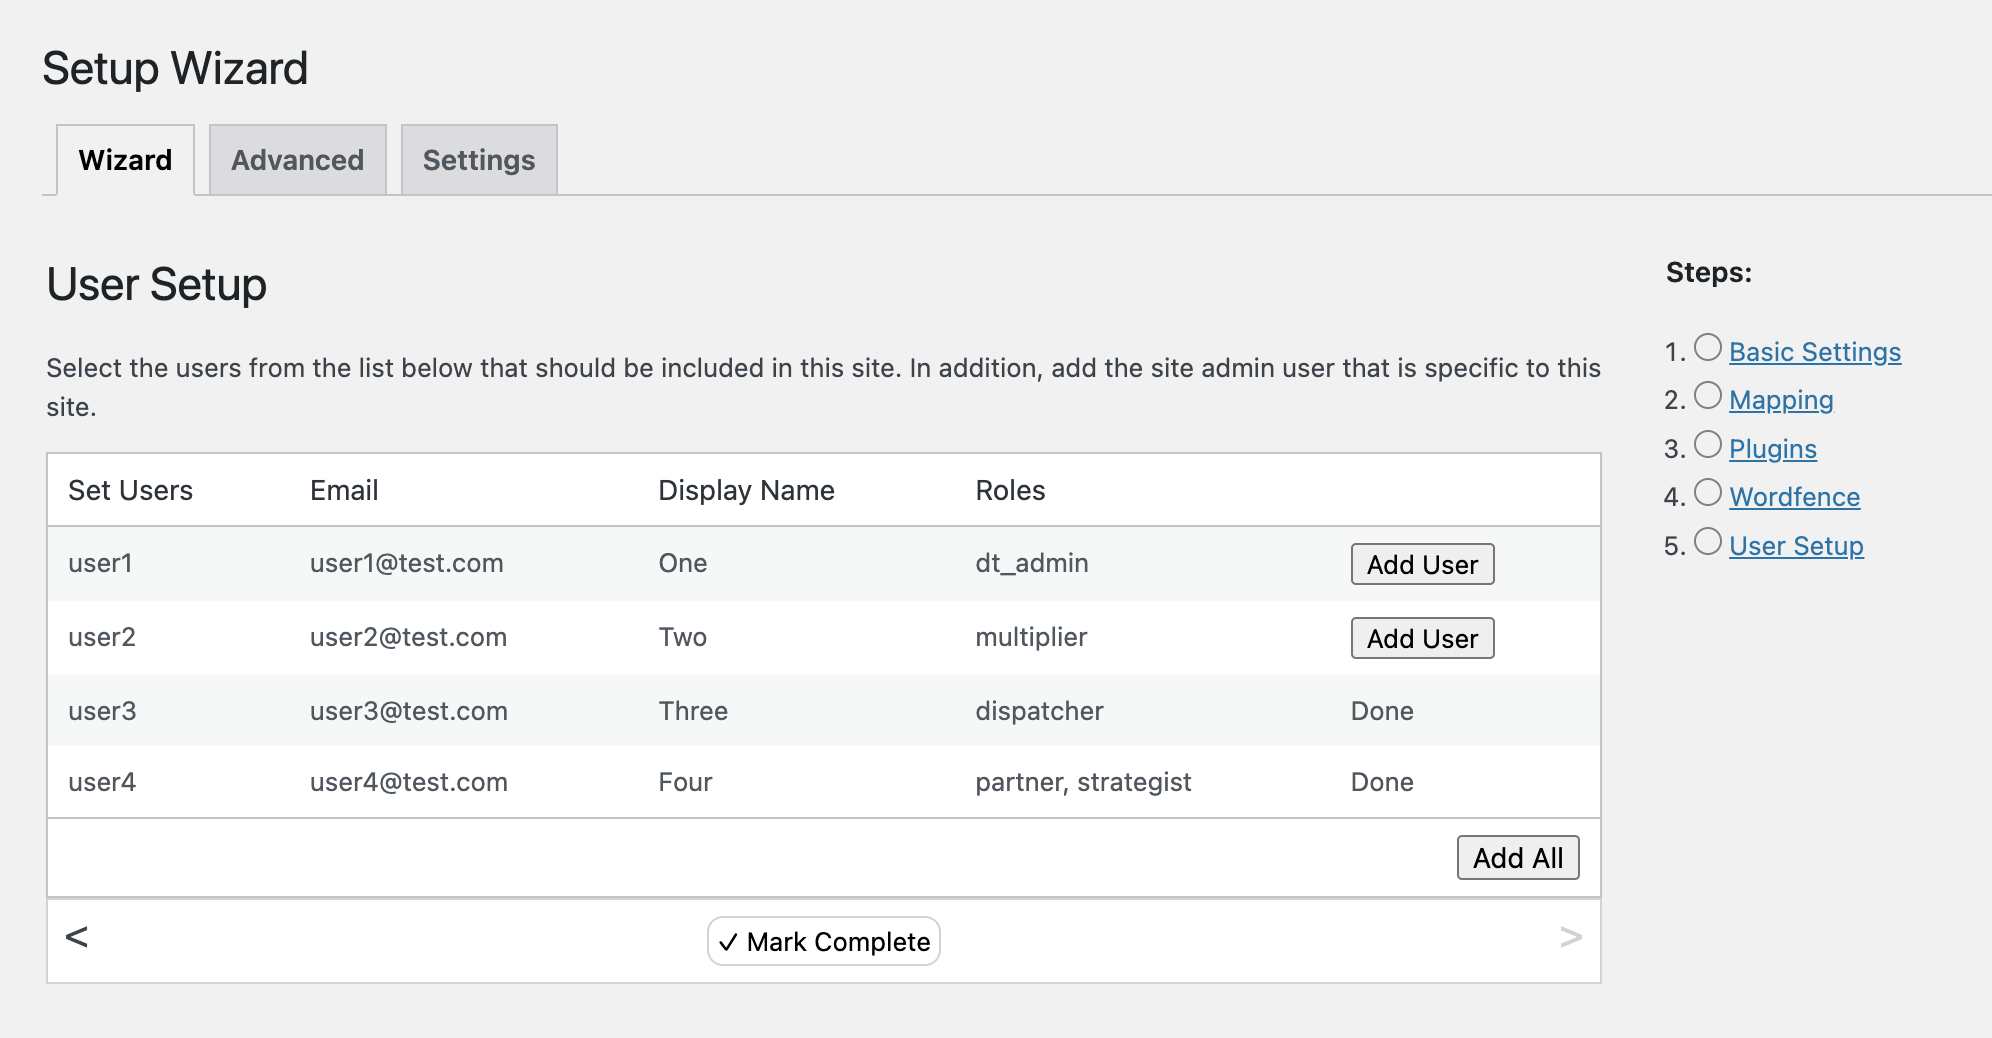
  • Show wizard step to add users
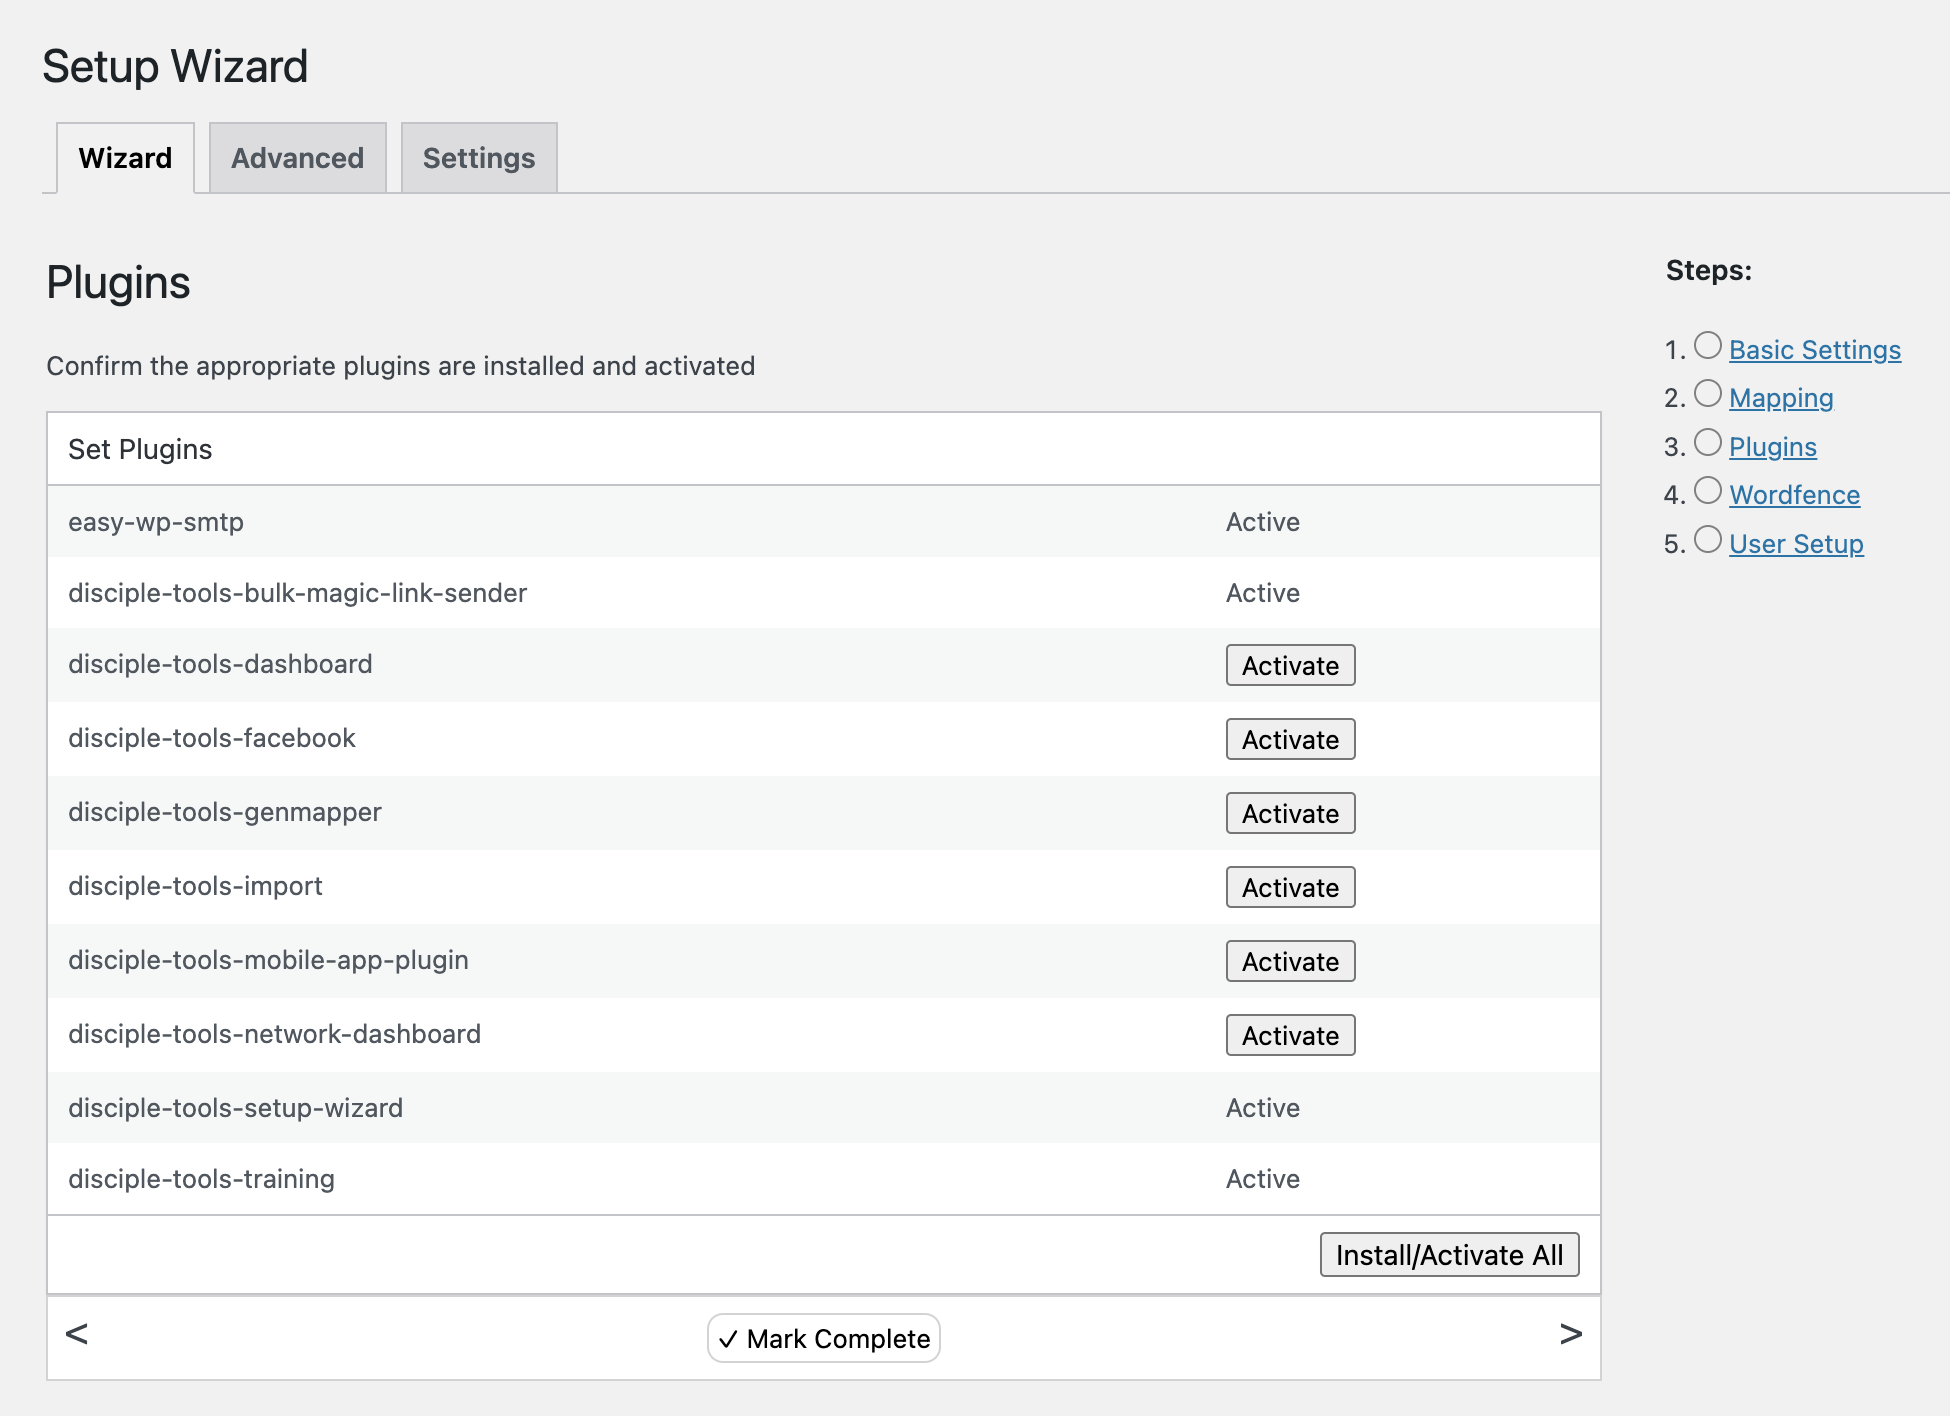
  • Show wizard step to install/activate plugins
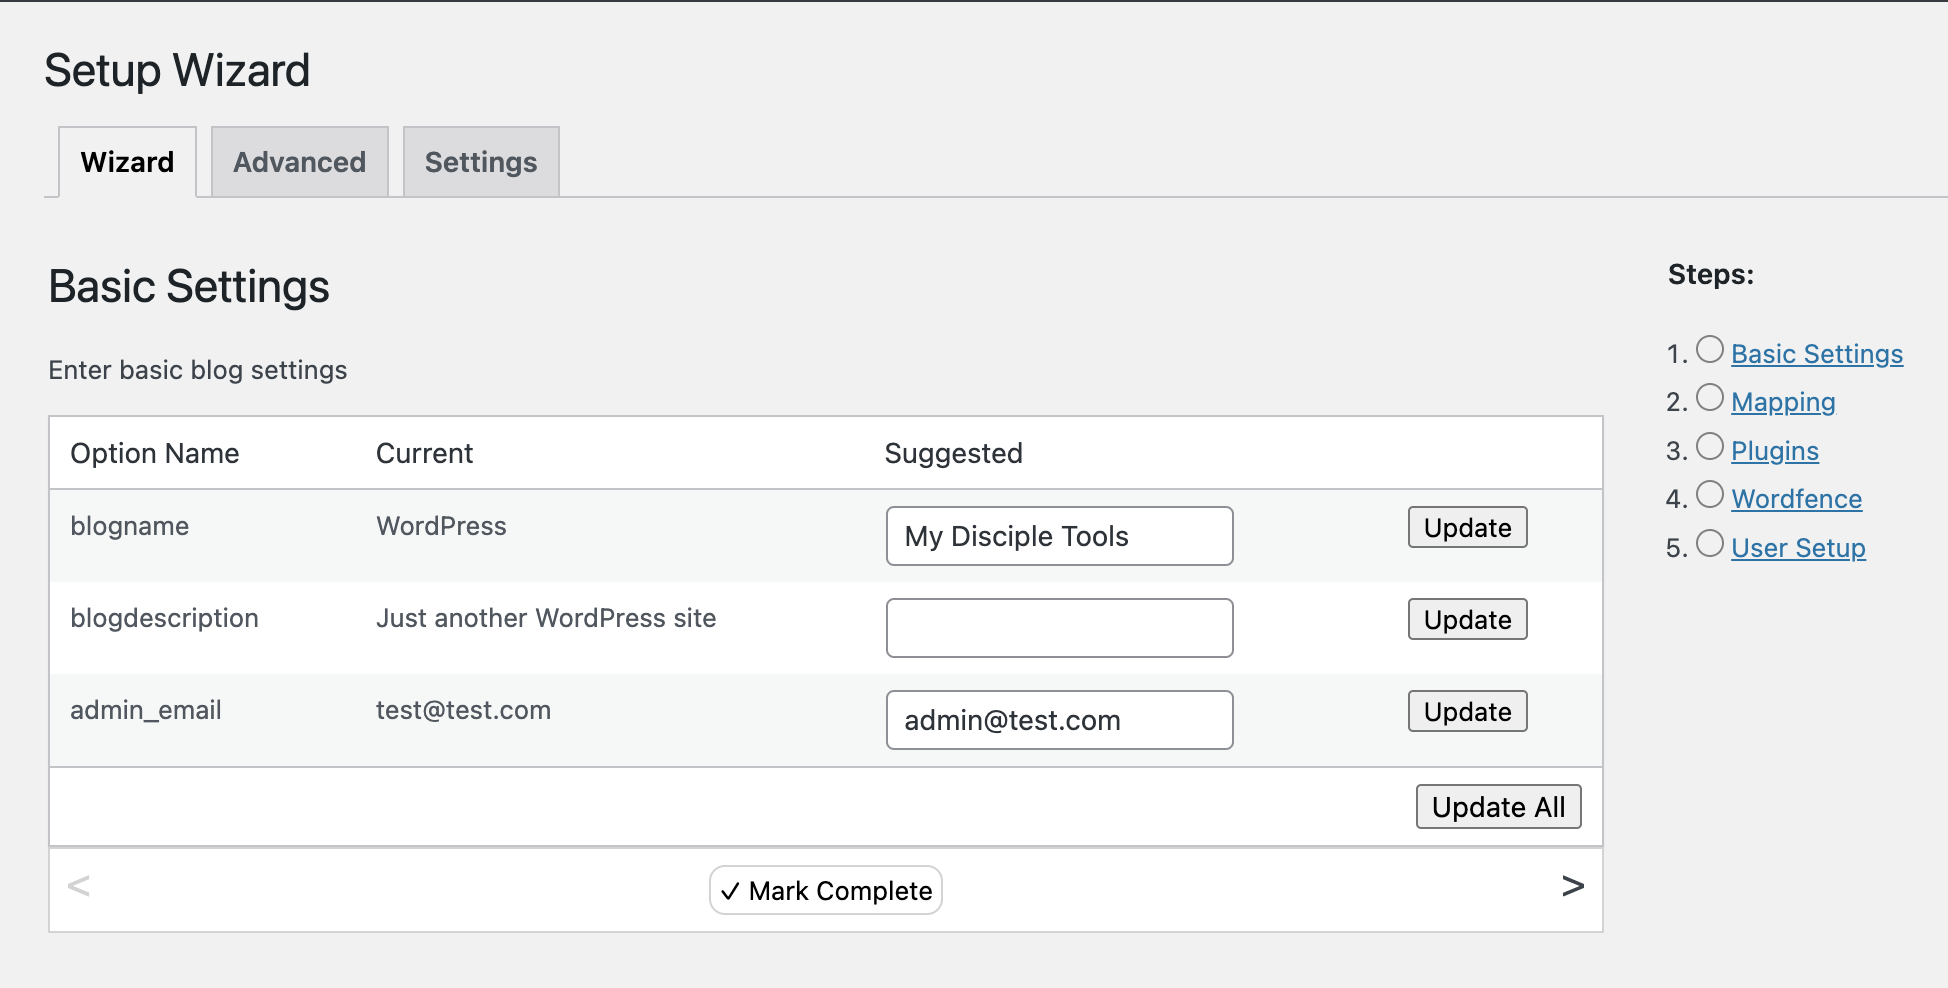
  • Show wizard step to set WP options
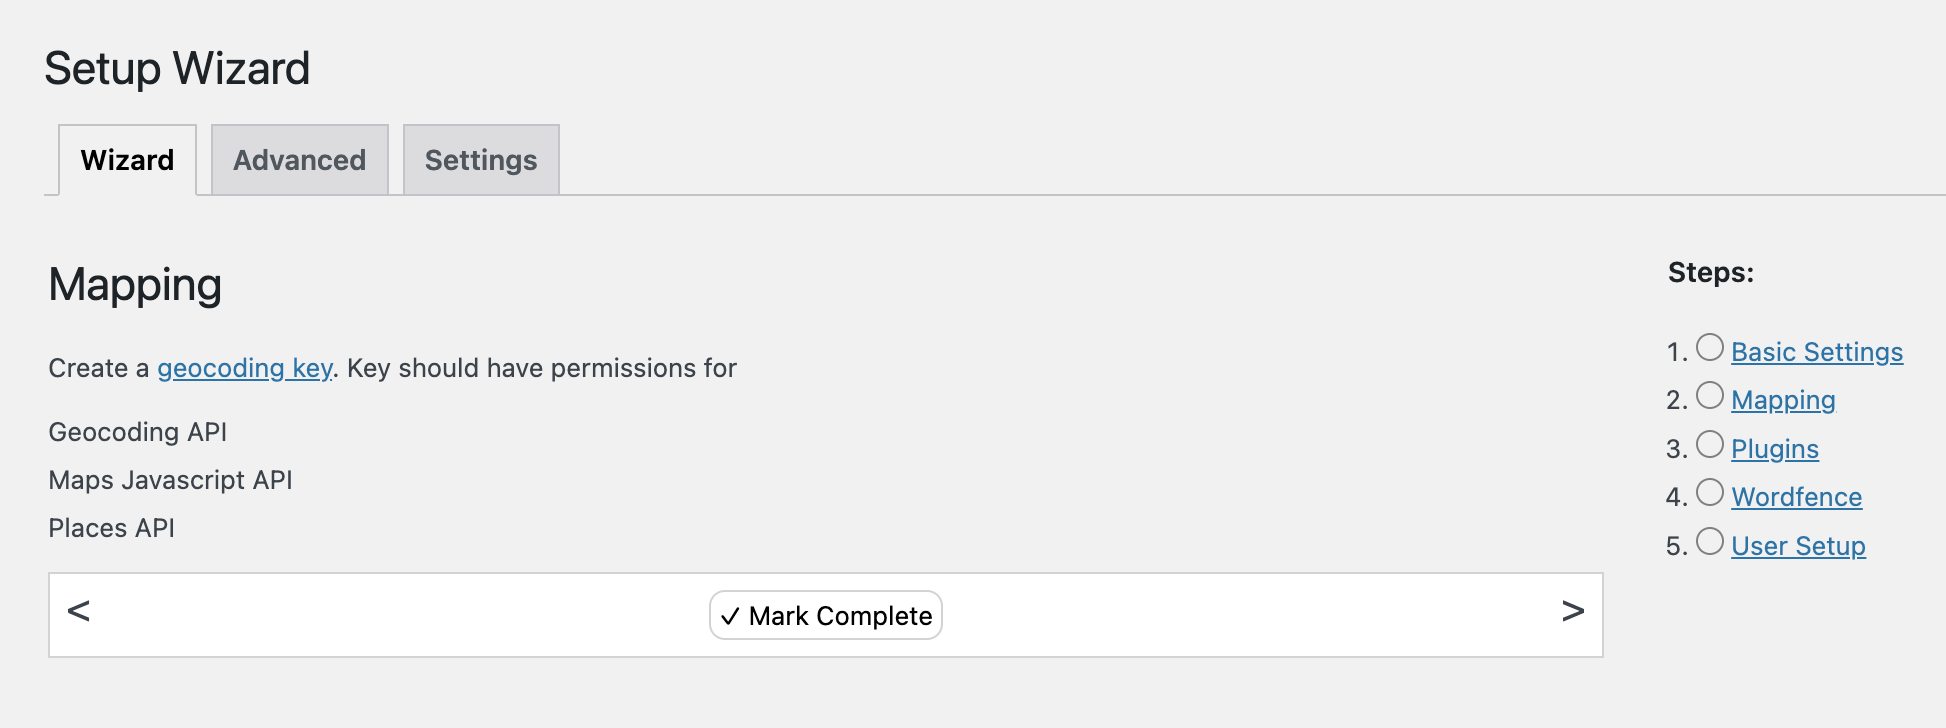
  • Show wizard step with markdown formatted text, including external links

Will Not Do

  • Friendly UI to generate JSON configuration

Requirements

  • Disciple.Tools Theme installed on a Wordpress Server

Installing

  • Install as a standard Disciple.Tools/Wordpress plugin in the system Admin/Plugins area.
  • Requires the user role of Administrator.

Contribution

Contributions welcome. You can report issues and bugs in the Issues section of the repo. You can present ideas in the Discussions section of the repo. And code contributions are welcome using the Pull Request system for git. For a more details on contribution see the contribution guidelines.

Screenshots

Step Type - Options
wizard-step-options.png
Step Type - Text
wizard-step-text.png
Step Type - Plugins
wizard-step-plugins.png
Step Type - Users
wizard-step-users.png

Credits

  • Project icon
    • “Wizard Hat” icon by mangunkarsa, from thenounproject.com
    • “config” icon by empat, from thenounproject.com

Releases

6 releases. Each count is every asset in that release; expand a row for the breakdown.

Tag
Published
Assets
Downloads
v1.0.2 latest
Jul 25, 2024 2 years ago
disciple-tools-setup-wizard.zip
69
Jun 7, 2024 2 years ago
disciple-tools-setup-wizard.zip
27
Jun 6, 2024 2 years ago
disciple-tools-setup-wizard.zip
24
May 15, 2023 3 years ago
disciple-tools-setup-wizard.zip
9
May 15, 2023 3 years ago
disciple-tools-setup-wizard.zip
4
Mar 9, 2023 3 years ago
disciple-tools-setup-wizard.zip
5

Active-site estimate ≈10 comes from the median of recent superseded releases. Method.

D+ grade

Security

Disciple.Tools - Setup Wizard 1.0.2 · audited by WP Registry

High-severity findings.

1 high 1 medium
Audited release
1.0.2
Findings
2
Worst severity
high
Content hash
4e7c15b7a73851ea2b2ac9b0…

Findings

  • high Authenticated (manage_dt / D.T Admin) arbitrary update_option via REST /option

    missing_capability

    Disciple_Tools_Setup_Wizard_Endpoints registers POST /wp-json/disciple-tools-setup-wizard/v1/option with permission_callback has_permission(), which is only current_user_can('manage_dt'). option_set() sanitizes the key then passes the raw value to update_option() with no allowlist or denylist. Array values default to array_replace_recursive() merge into the existing option unless overwrite=true, so a caller can graft capabilities onto {prefix}user_roles. Disciple.Tools documents Manage D.T (dt_admin) as customizing DT settings/plugins and explicitly not Manage WP; the theme's own dt-admin-settings/update-dt-options skips any key that does not start with dt_. This plugin's sample config does set blogname/admin_email, but the endpoint also accepts users_can_register, default_role=administrator, siteurl, home, active_plugins, template/stylesheet, and {prefix}user_roles. Subscriber cannot call it. A D.T Admin (no manage_options) can. REST cookie auth still requires X-WP-Nonce, so this is not unauthenticated CSRF; it is a missing-authorization primitive relative to the capability the action requires.

    rest-api/rest-api.php:15-74,86-94

    Recommendation

    Keep permission_callback on manage_dt (or raise it to manage_options for WP-core keys). Allow-list option keys the wizard is meant to set (blogname, blogdescription, admin_email, dt_setup_wizard_config, dt_setup_wizard_progress, and other explicit dt_* keys). Reject users_can_register, default_role, siteurl, home, active_plugins, template, stylesheet, {prefix}user_roles, and any key the current user cannot change via current_user_can('manage_options'). Do not merge arbitrary arrays into existing options. Mirror the theme's strpos($option_key, 'dt_') !== 0 continue guard for DT-only writes.

  • medium Stored admin XSS via innerHTML of wizard config slugs, option keys, and usernames

    xss_stored

    createMessageLi assigns attacker-influenced strings to li.innerHTML. showMessage is called with plugin['slug'], option.key, and user.username taken from dt_setup_wizard_config (written through option_set / the Settings JSON form by any manage_dt user) or from the Advanced JSON runner. PHP echoes those values through esc_html into hidden inputs; the browser HTML-decodes them, JSON.parse restores the original string, and innerHTML then parses markup. <script> tags would not run via innerHTML, but event-handler injection (<img src=x onerror=…>, <svg onload=…>) does. The page is wp-admin Setup Wizard, reachable by dt_admin and by WP administrators who also have manage_dt. A D.T Admin can plant the payload in the shared config and have it execute in a full administrator's session when that admin clicks Install, Update, or Add User. No frontend consumer.

    admin/js/wizard.js:387-409

    Recommendation

    Set textContent (or document.createTextNode) instead of innerHTML in createMessageLi. Treat config-derived slugs, keys, and usernames as untrusted even for manage_dt authors. If HTML is required, pass the string through a sanitizer that strips event handlers. Validate plugin slugs against ^[a-z0-9_-]+$ before render or install.

WP Registry hashes the installable build and reports on that exact bytes-for-bytes copy. Embargoed findings are withheld until they are disclosed, so a clean verdict means nothing public is outstanding. WP Manifest does not audit code itself.