WP Manifestindependent plugin directory
manifest / admin / bh-wp-plugins-page

Plugins Page Cleanup WP Registry grade B. Medium-severity findings · 1 findingWP RegistryMedium-severity findings · 1 findingOpen the reportB

Tidies up common annoyances in WordPress admin's plugins page.

★ 6stars
125release downloads
≈10active sites
1.4.1latest · 1mo ago

Install

Download bh-wp-plugins-page.1.4.1.zip From the 1.4.1 release on GitHub, Sep 3, 2026

Upload it under Plugins → Add New Plugin → Upload Plugin, then activate.

Install straight from GitHub with WP-CLI:

wp plugin install https://github.com/brianhenryie/bh-wp-plugins-page/releases/download/1.4.1/bh-wp-plugins-page.1.4.1.zip
No built-in updater. New versions won't appear under Dashboard → Updates. Install new releases yourself, or let Git Updater track the repository.

Cleans up WordPress's plugins.php.

Description

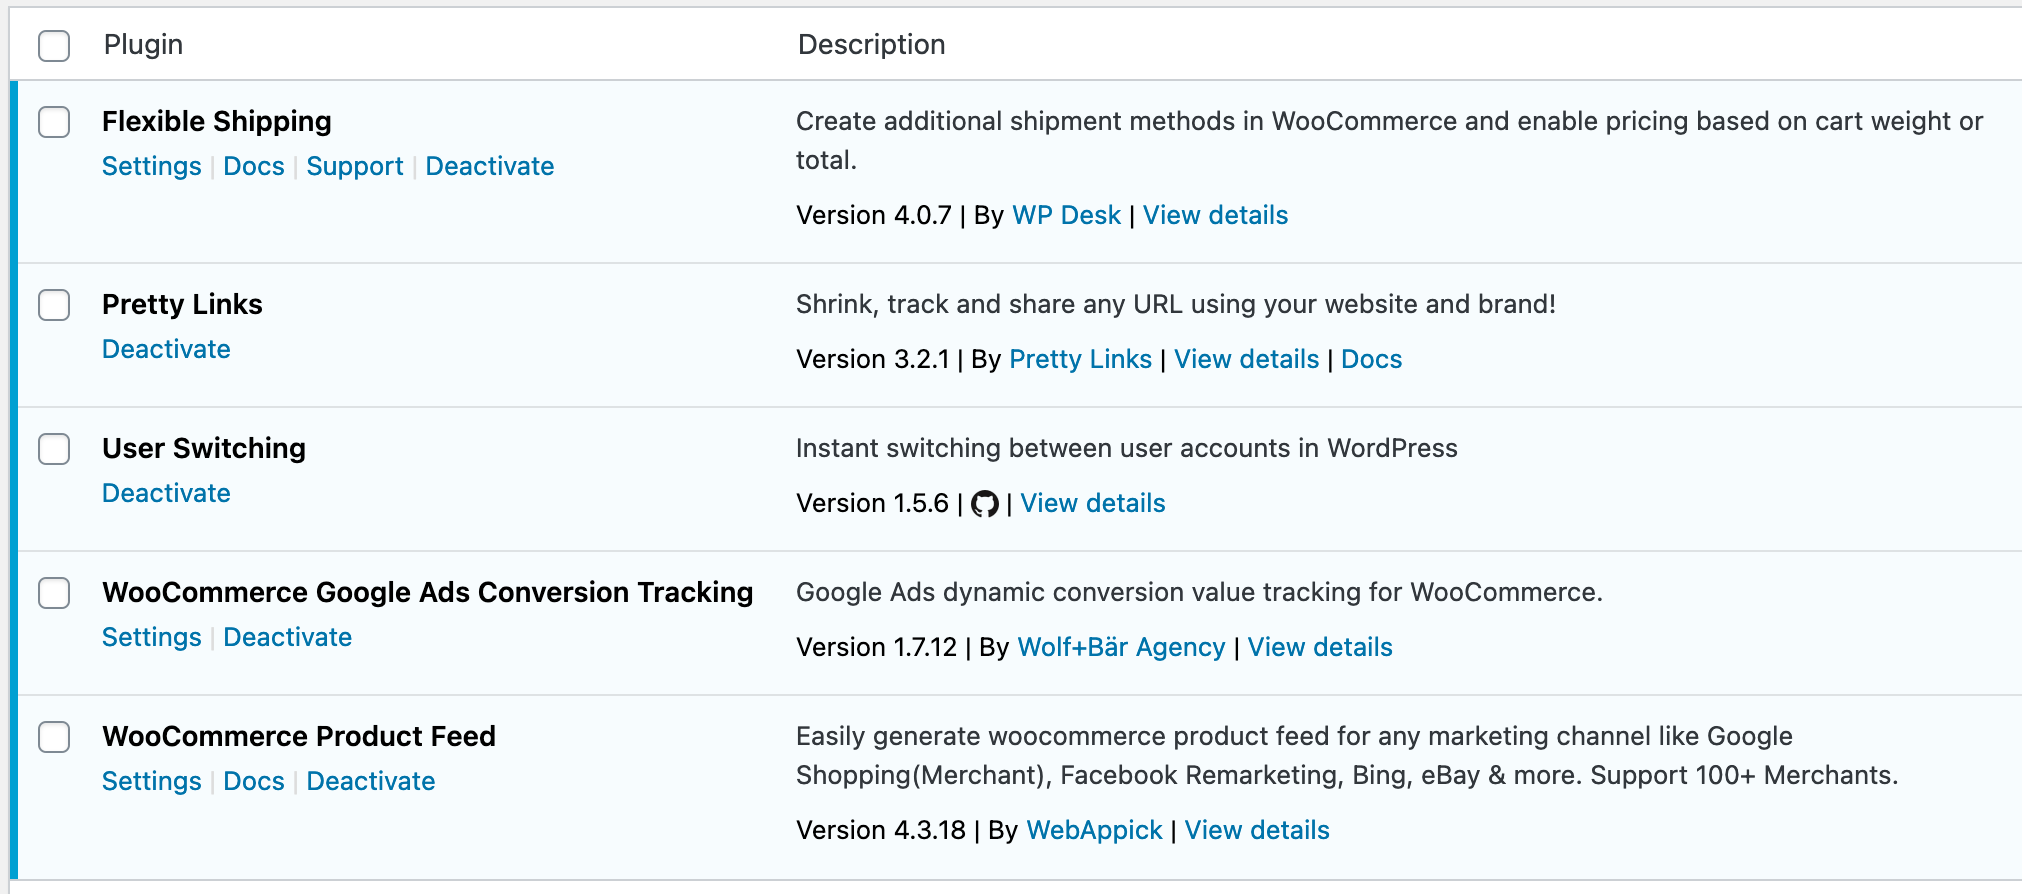
  • Removes formatting from links
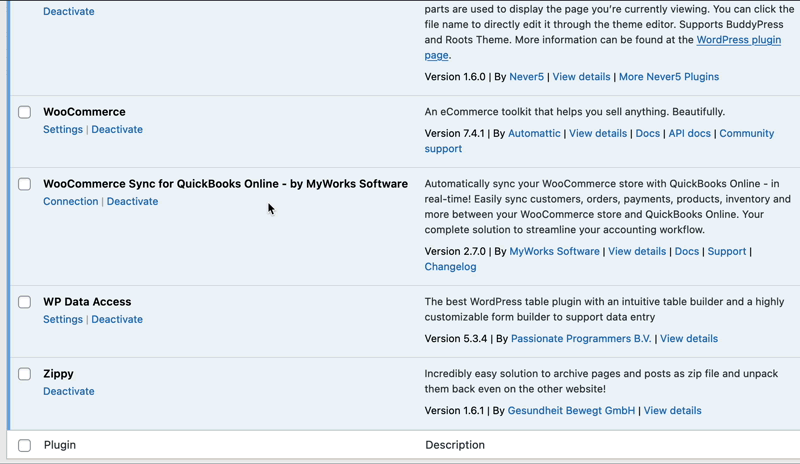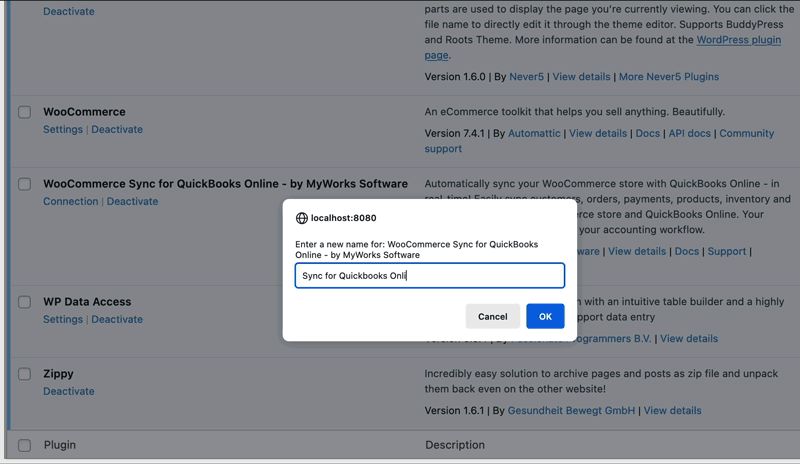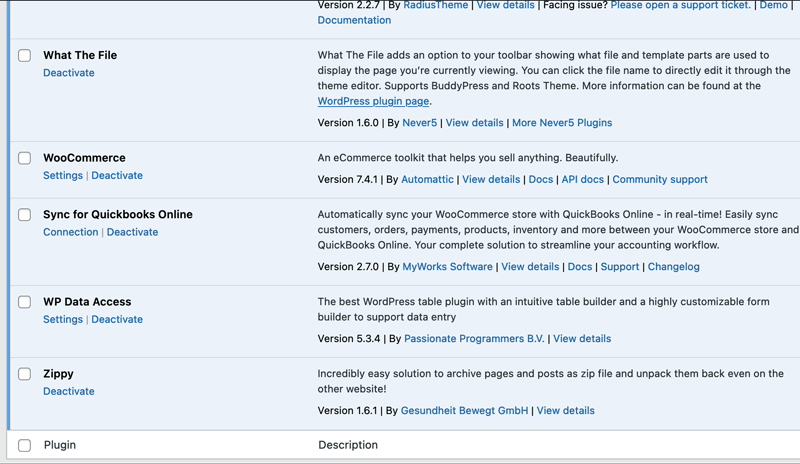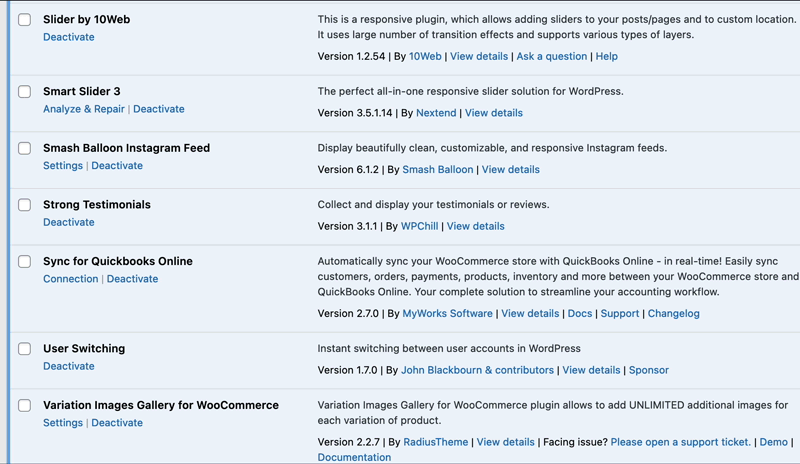
  • Allows renaming plugin titles
  • Prevents redirecting away from plugins.php on plugin activation
  • Moves external links from the action links (first) column into the description column, and vice-versa
  • Moves deactivate to the end of the list of action links, and settings to the beginning (where it exists)
  • Replaces GitHub links with icons
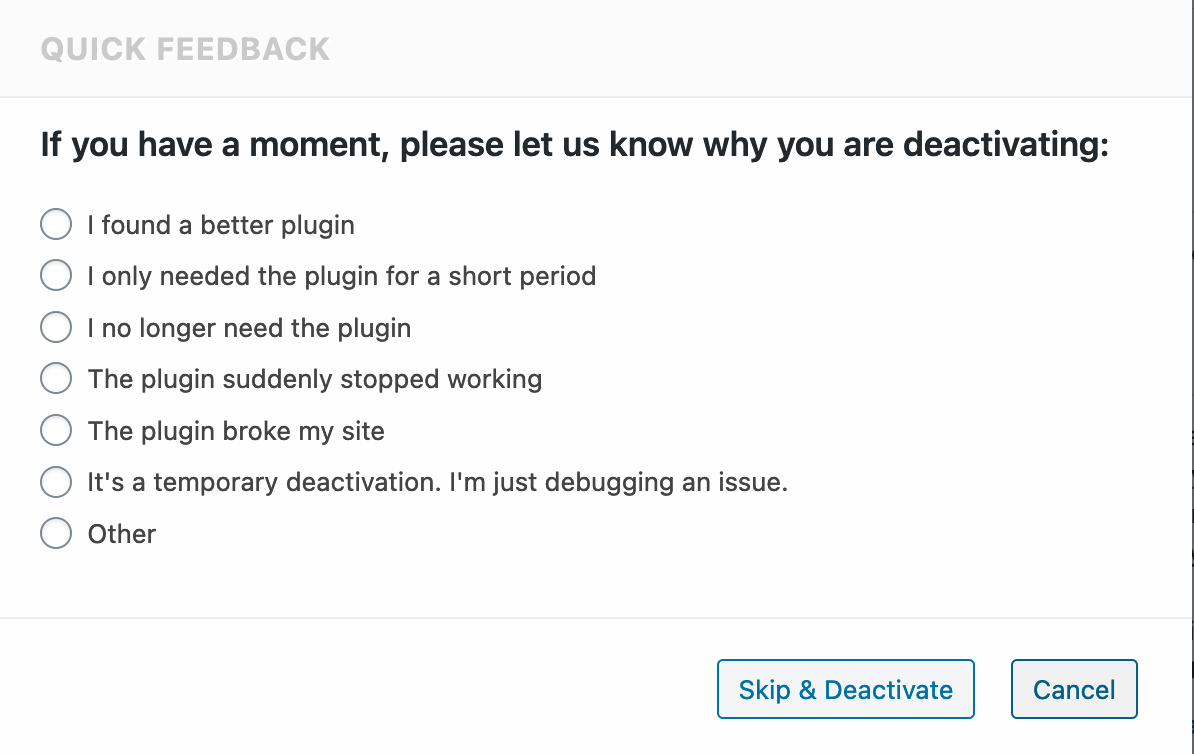
  • Removes click handlers on Deactivate links (to remove deactivation surveys)

Before: Before
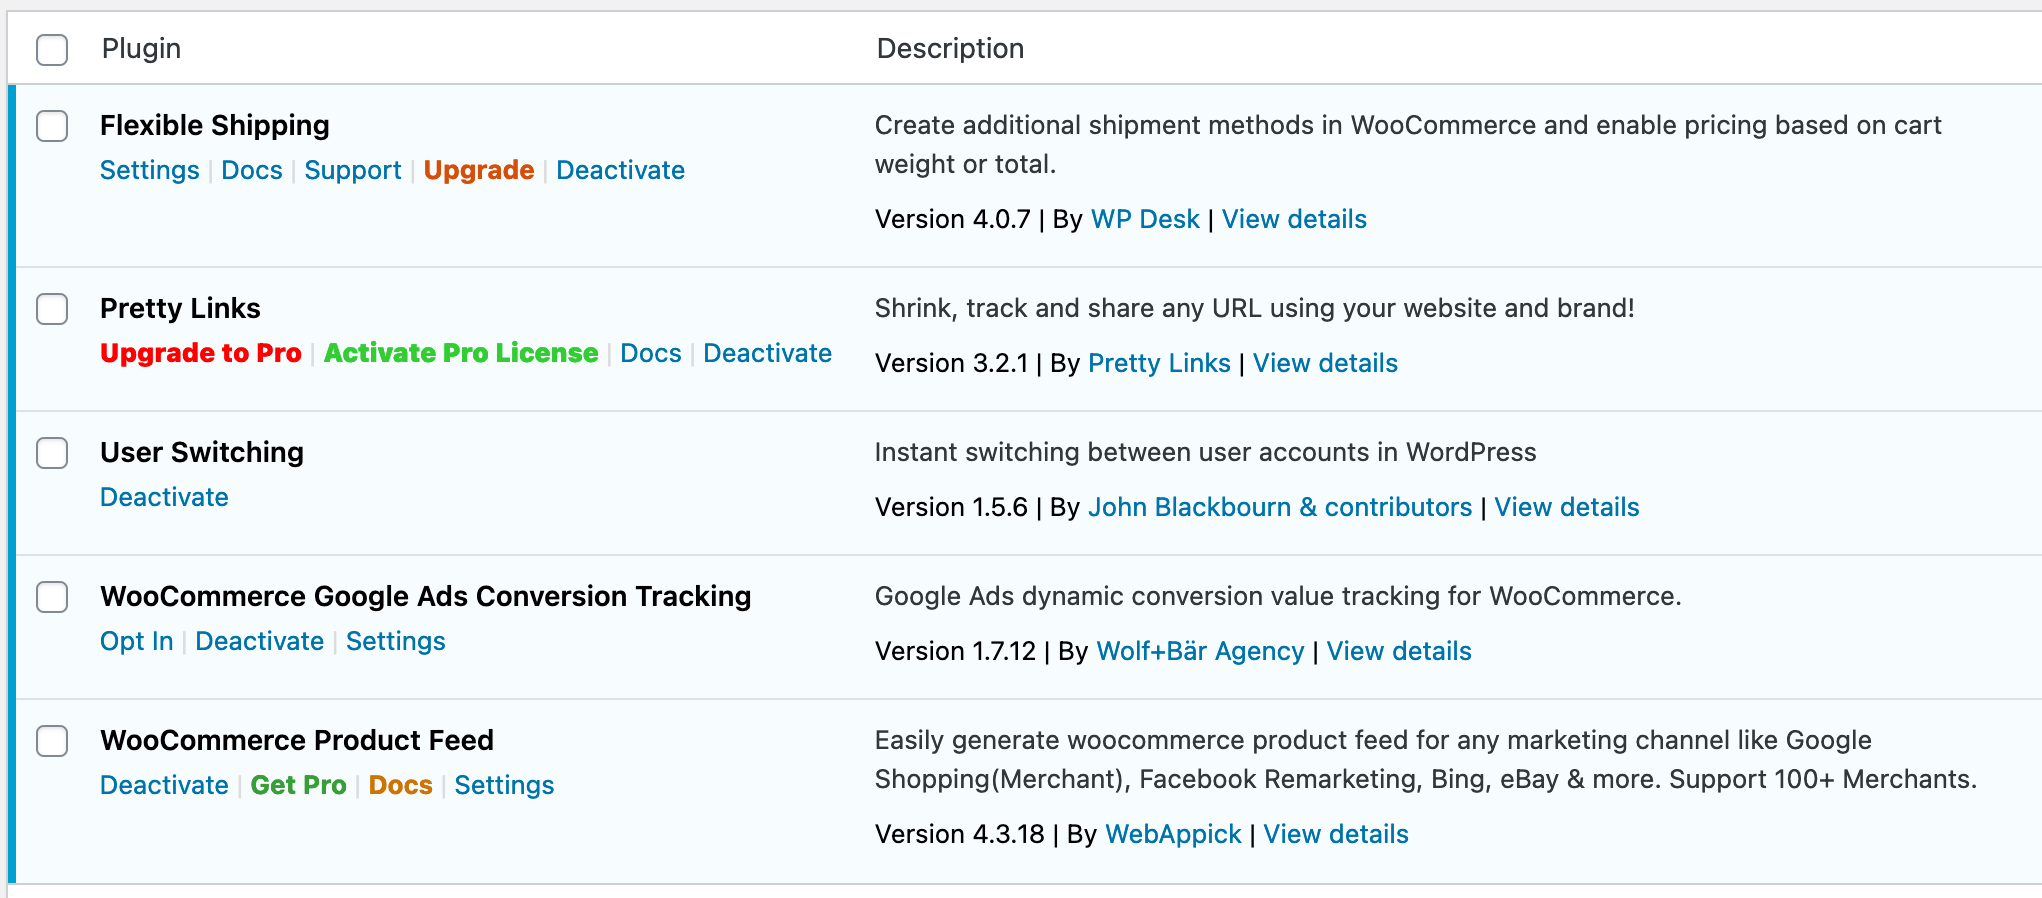
After: After

Rename plugins:

Rename

Removes JavaScript hooked to deactivation buttons to prevent these: Deactivate
Installation

Download the latest release.

TODO:

  • Set a max-length on plugin titles (line-break) so the description column isn't too cramped. Added renaming.
  • When removing a Licence link, add an admin notice for a few days so users can still easily access the page.
  • Add a UI for adding Settings links for plugins that don't have them
  • Add installed date and last updated date on each plugin
  • Logs should go before Deactivate, never ahead of anything else.
  • Reconsider use of PHP_INT_MAX in actions.

More Information

See github.com/BrianHenryIE/WordPress-Plugin-Boilerplate for initial setup rationale.

Acknowledgements

I was finally promoted to write this after seeing someone (Timbr) complain about this same irritating problem on Discord.

Releases

13 releases. Each count is every asset in that release; expand a row for the breakdown.

Tag
Published
Assets
Downloads
1.4.1 latest
Sep 3, 2026 1mo ago
bh-wp-plugins-page.1.4.1.zip
3
Feb 15, 2026 8mo ago
bh-wp-plugins-page.1.4.0.zip
10
Apr 28, 2023 3 years ago
bh-wp-plugins-page.1.2.0.zip
26
Mar 1, 2023 3 years ago
bh-wp-plugins-page.1.2.0.zip
13
Oct 20, 2022 4 years ago
bh-wp-plugins-page.1.1.1.zip
10
Sep 28, 2022 4 years ago
bh-wp-plugins-page.1.1.0.zip
9
Apr 27, 2022 4 years ago
bh-wp-plugins-page.1.0.9.zip
12
Sep 15, 2021 5 years ago
bh-wp-plugins-page.1.0.7.zip
9
Sep 9, 2021 5 years ago
bh-wp-plugins-page.1.0.5.zip
8
Jan 26, 2021 5 years ago
bh-wp-plugins-page-1.0.3.zip
8
Jan 23, 2021 5 years ago
bh-wp-plugins-page-1.0.2.zip
5
Jan 17, 2021 5 years ago
bh-wp-plugins-page-1.0.1.zip
6
Jan 17, 2021 5 years ago
bh-wp-plugins-page-1.0.0.zip
6

Active-site estimate ≈10 comes from the median of recent superseded releases. Method.

B grade

Security

Plugins Page Cleanup 1.4.1 · audited by WP Registry

Medium-severity findings.

1 medium
Audited release
1.4.1
Findings
1
Worst severity
medium
Content hash
c384e2f2913a1e6a9a65a4c5…

Findings

  • medium Log files written under wp-content/uploads/logs are world-readable on nginx and non-permalink Apache

    information_disclosure

    Logger::instance() always opens a Monolog StreamHandler at WP_CONTENT_DIR/uploads/logs/{slug}-{Y-m-d}.log (default level INFO). Protection is delegated to bundled bh-wp-private-uploads, which (1) uses an empty post type so REST/media hooks are skipped, (2) writes only an index.php guard — the library comments that a deny-all .htaccess would 403 authorised PHP downloads — and (3) registers an Apache external rewrite of uploads/logs/(.*) to index.php?-private-uploads-file=$1 plus Serve_Private_File on init (manage_options). Two wrapping bugs make that fail on common installs: instantiate_bh_wp_plugins_page() returns immediately unless is_admin() || wp_doing_ajax(), so Serve_Private_File, the hourly is-private HTTP probe, and delete_logs_{slug} cron are never registered on front-end or wp-cron.php requests; and maybe_flush_rewrite_rules() refuses to write .htaccess unless pretty permalinks, mod_rewrite, and a non-AJAX admin load are all true. nginx/OpenLiteSpeed/IIS serve the existing .log as a static file (predictable URL /wp-content/uploads/logs/bh-wp-plugins-page-YYYY-MM-DD.log) without ever hitting PHP. ERROR/WARNING entries include debug_backtrace. On multisite the write path (WP_CONTENT_DIR/uploads/logs) also diverges from the rewrite target (wp_upload_dir() basedir, typically uploads/sites/{id}/logs), so even a working Apache rule protects the empty directory.

    vendor-prefixed/brianhenryie/bh-wp-logger/includes/class-logger.php:117-206

    Recommendation

    Write logs outside the web root (or under a randomly named directory that is not mapped as a static alias). Emit a directory-level deny (Apache Require all denied / nginx location deny) independent of permalinks, and use wp_upload_dir()['basedir'] consistently so the rewrite target matches the files. Remove the is_admin()/AJAX-only bootstrap around Logger::instance() so Serve_Private_File and the is-private cron actually run on front-end and wp-cron.php. Add current_user_can('manage_options') next to the existing nonces on the logger delete/download handlers.

WP Registry hashes the installable build and reports on that exact bytes-for-bytes copy. Embargoed findings are withheld until they are disclosed, so a clean verdict means nothing public is outstanding. WP Manifest does not audit code itself.